
An air gapped backup is an offline copy of critical data deliberately isolated from networks to stop remote tampering. Use one when you need a last line of defence against destructive ransomware or a site-wide disaster. Both CISA and the Australian Cyber Security Centre (ACSC) recommend offline, encrypted backups as a foundational control precisely because they interrupt the attacker’s path to your data entirely. Techbug’s managed backup engagements consistently show that organisations without a tested offline copy face the longest recovery times after a ransomware incident.
Quick pros and cons:
- Ransomware resilience: a physically or logically disconnected copy cannot be encrypted by malware running on your network.
- Data integrity: isolation prevents silent corruption or deletion by a compromised account.
- Last-line recovery: when every other layer fails, an air gapped copy is what gets you back online.
- Cost and complexity: physical media, secure transport, and manual processes add real overhead.
- Restore latency: retrieving data from offline storage takes longer than pulling from a live cloud volume.
- Operational discipline: without rigorous rotation and testing schedules, the gap becomes a liability rather than an asset.
The distinction between an air gap, an immutable backup, and a standard offline copy matters here. An immutable backup stays network-accessible but cannot be altered or deleted for a set retention window. An air gapped backup goes further: it is completely disconnected, so an attacker with full network access still cannot reach it. A standard offline copy achieves similar isolation but may lack the procedural controls and encryption that make an air gap genuinely trustworthy.
Table of Contents
- What does “air gapped backup” actually mean, and what types exist?
- Air gapped vs immutable vs offline backups: which should you choose?
- Why ransomware makes air gapped backups a business-critical control
- Practical design checklist for air gapped backups in Australia
- How to validate your air gapped backups and measure recovery readiness
- Operational limitations and common mistakes that undermine air gapped backups
- Retention, data sovereignty and compliance in Australia
- What does it cost, and how long does deployment take?
- When air gapped backup strategies have failed: lessons from real incidents
- Key takeaways
- The gap between theory and practice in Australian SMB deployments
- Techbug protects Australian businesses with ransomware-safe backup strategies
What does “air gapped backup” actually mean, and what types exist?
Air gapped backups can be physical, logical, or provider-operated cloud air gaps, and each approach trades isolation level against operational convenience differently. Understanding the distinctions helps IT teams pick the right architecture before committing to hardware or contracts.
Physical air gaps
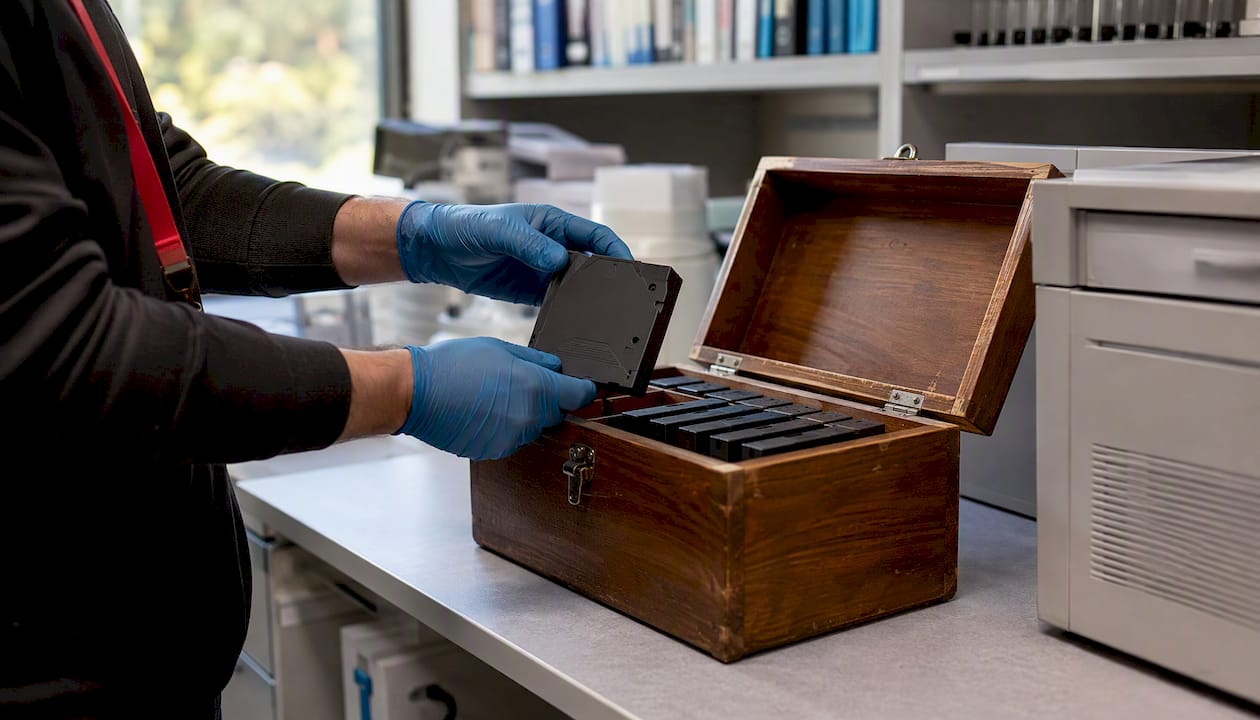
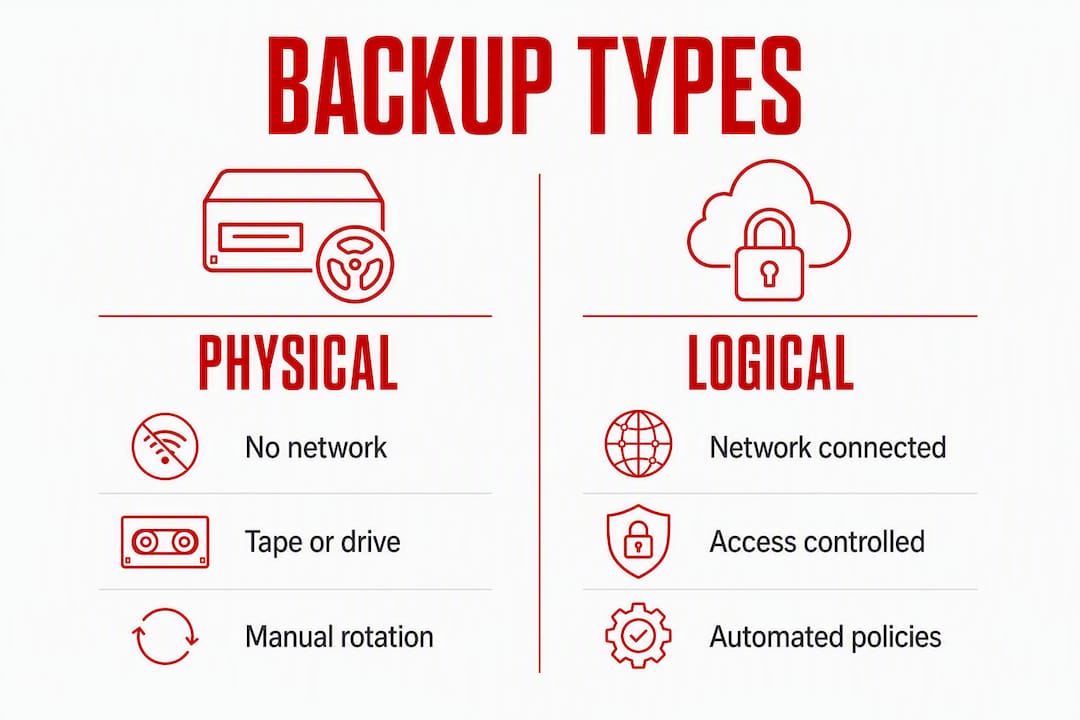
A physical air gap means the backup media has no network connection at all. Tape cartridges written on-site and transported to a secure offsite vault are the classic example. LTO tape, external hard drives stored in a fireproof safe, or optical discs all qualify. The isolation is absolute: there is no network path an attacker can exploit. The trade-off is that every step, writing, labelling, transporting, and retrieving, is manual.
Logical air gaps
A logical air gap keeps the storage infrastructure network-connected but enforces strict separation through access controls, network segmentation, and immutable storage policies. The backup repository sits in an isolated VLAN or a hardened cloud vault that production systems cannot reach directly. Physical air gaps provide the highest network isolation but introduce manual processes and restore delays; logical air gaps are more automatable but require strong controls. For most Australian SMBs, a well-implemented logical air gap delivers a practical balance between security and speed.
Cloud-based air gaps
Cloud providers offer managed vault services where backup data is replicated to a separate tenancy or region with no direct network path from the production environment. The provider manages the isolation layer. Restore speed depends on internet bandwidth, and you are trusting the provider’s isolation architecture, so vendor due diligence matters.
Hybrid approaches
A hybrid approach layers physical and logical controls: for example, daily backups to a logically isolated cloud vault, with weekly or monthly copies written to tape and stored offsite. This covers both rapid recovery from the logical copy and ultimate resilience from the physical one.
| Type | Isolation level | Automation | Restore speed | Operational effort |
|---|---|---|---|---|
| Physical (tape/drive offsite) | Highest | Low | Slow (hours to days) | High |
| Logical (isolated vault/VLAN) | High | High | Fast (minutes to hours) | Medium |
| Cloud air gap (provider vault) | High | High | Medium (bandwidth-dependent) | Low to medium |
| Hybrid (logical + physical) | Highest | Medium | Variable | High |
Air gapped vs immutable vs offline backups: which should you choose?
Air gapped backups are completely disconnected and therefore interrupt the attacker’s path to backup data; immutable backups remain accessible but protect data from being altered or deleted for a set window. That single difference drives most of the decision logic.
Accessibility during recovery: immutable backups are online and can be restored in minutes. Air gapped copies require retrieval from offline media or a separate vault, adding time. For workloads with an RTO measured in minutes, immutability alone may be sufficient. For workloads where the entire production environment could be compromised, including the backup management plane, only a disconnected copy is safe.
Protection surface: immutability protects against deletion and encryption but does not protect against an attacker who can wait out the retention window or who compromises the storage admin account. An air gap removes the network vector entirely.
Typical storage locations:
- Immutable: object storage with WORM (Write Once Read Many) policies, cloud blob storage with retention locks.
- Air gapped (physical): LTO tape, external drives, optical media in offsite vaults.
- Air gapped (logical): isolated cloud tenancies, hardened backup repositories with no production network path.
Decision criteria:
- Choose immutability when RTO is tight, automation is a priority, and your threat model centres on ransomware that cannot compromise admin credentials.
- Choose a physical air gap when you need absolute network isolation, face regulatory requirements for offline retention, or are protecting long-term archives.
- Choose a logical air gap when you want automation and faster restores but still need strong separation from production systems.
- Choose a hybrid when the dataset is critical enough that no single failure mode should be able to destroy all copies.
Pro Tip: Combine controls rather than choosing one. A logical air gap with WORM policies and a monthly physical tape copy gives you fast automated recovery for most incidents and an ultimate fallback for catastrophic ones. This layered approach aligns with the 3-2-1 rule: three copies, two media types, one offsite.
Why ransomware makes air gapped backups a business-critical control
Three threat scenarios explain most of the risk that air gapped backups are designed to address.
Destructive ransomware that targets backups first. Modern ransomware variants actively hunt for backup software, shadow copies, and connected backup repositories before triggering encryption. If your backup agent is reachable from the infected host, the attacker deletes or encrypts your backups before you know the attack has started. An air gapped copy has no network address to target.
Insider sabotage or compromised admin credentials. A malicious insider or an attacker who has stolen privileged credentials can modify backup schedules, delete restore points, or corrupt backup metadata through the management console. If the management console that orchestrates backups remains network-connected and is compromised, attackers can modify or delete offline-target schedules or attached metadata. A physically isolated copy is immune to this vector.
Site-wide physical disaster. Fire, flood, or a building-level power event can destroy on-premises infrastructure simultaneously. An offsite air gapped copy, whether tape in a vault or a geographically separate cloud region, survives the physical event.
Mapping scenarios to business priorities. Not every dataset warrants the cost of a physical air gap. Map your critical services to RTO and RPO targets first. Financial records, patient data, system images for core servers, and legal documents typically justify the overhead. Development environments and non-critical file shares usually do not.
Industries where air gapped backups are commonly required or strongly recommended in Australia include financial services (APRA CPS 234 obligations), healthcare (My Health Records Act, state health privacy legislation), legal firms, and any organisation subject to the Privacy Act 1988 and the Notifiable Data Breaches scheme.
Practical design checklist for air gapped backups in Australia
An air gap is best treated as a strategy rather than a single product: an end-to-end recovery process is required, with documented and tested procedures. The checklist below gives you a starting framework.
Storage and media selection
- Select media appropriate to your retention period: LTO tape for long-term archives with a rated lifespan of several years, external drives for shorter cycles, or a logically isolated cloud vault for automated daily copies.
- Label every piece of media with the backup date, dataset scope, encryption key reference, and responsible owner.
- Store physical media in a fireproof, waterproof container at a secure offsite location sufficiently distant from the primary site.
- Maintain a media register that tracks every cartridge or drive: location, creation date, last verified date, and scheduled destruction date.
Encryption and key management
- Encrypt backups at rest on offline media with AES-256 prior to transit and store encryption keys separately from the media to protect data if physical media is stolen or intercepted.
- Store master encryption keys in a hardware security module (HSM) or a separate key management service with access logging.
- Document the key retrieval process in the restore runbook so recovery is not blocked by a missing passphrase.
Access controls and management console hardening
- Secure the management console with out-of-band MFA and strict RBAC; no production account should have write access to the backup repository.
- Limit the number of accounts with the ability to delete or modify backup jobs to the minimum required.
- Enable immutable audit logging for all backup and restore operations; ship logs to a separate, write-protected destination.
- Isolate the backup management network from the production network using a dedicated VLAN or out-of-band management interface.
Transport procedures
- Use tamper-evident packaging for physical media in transit.
- Log every transport event: who moved the media, when, and to where.
- Never leave media unattended in a vehicle or unsecured location during transit.
Sample restore runbook outline
Preconditions: confirm the incident scope, identify the target restore point, verify media integrity hash, and confirm encryption key availability.
Isolation steps: disconnect affected systems from the network before beginning restore; stand up a clean restore environment (bare-metal or VM) with no connection to the compromised network.
Restore steps: mount or connect the air gapped media; run integrity verification before writing data; restore in priority order (OS images, then application data, then user data); document each step with timestamps.
Validation checks: confirm application functionality, verify data completeness against a known manifest, run antivirus and EDR scans on restored data before reconnecting to production.
Post-restore hardening: rotate all credentials that existed before the incident; patch the vulnerability that allowed the original compromise; update the runbook with any gaps discovered during the exercise.
Pro Tip: Rotate physical media on a schedule tied to your RPO. For example, multiple sets of media in rotation can ensure a single media failure does not leave you without a recent copy. Combine this with a daily logical air gap for rapid recovery and the physical copies for ultimate resilience.
How to validate your air gapped backups and measure recovery readiness
Verification and restore testing are the most common failure points; offline media can degrade and ‘set-and-forget’ air gaps often fail because restores are untested. A structured test plan closes that gap.
Test plan steps:
- Restore environment preparation: provision a clean, isolated VM or physical machine with no connection to production. Confirm the test environment matches the target OS and application versions.
- Staged restore: restore a single non-critical dataset first. Verify the process works end-to-end before committing to a full restore.
- Integrity verification: compare restored data against a known hash or manifest generated at backup time. Any mismatch is a failure.
- Full failover simulation: at least annually, simulate a complete production failure and restore all critical systems from the air gapped copy. Time the process against your RTO target.
- Clean-room ingestion: for ransomware scenarios, treat all restored data as potentially contaminated. Scan with updated endpoint protection before reconnecting to any network.
Key metrics to track:
- Restore success rate (target: 100% for critical datasets)
- Time-to-restore per dataset tier
- Integrity validation pass rate
- Number of restore attempts required before success
| Dataset criticality | Test type | Recommended frequency |
|---|---|---|
| Tier 1 (core systems, financial data) | Full restore simulation | Quarterly |
| Tier 2 (operational data, email) | Staged partial restore | Every 6 months |
| Tier 3 (archives, non-critical files) | Integrity hash verification | Annually |
| All tiers | Runbook walkthrough (tabletop) | Annually |
Guidance for vendors and system owners recommends a range of protections for backups to be considered ransomware-resistant, and emphasises regular testing and monitoring. Regular testing for Tier 1 datasets is a defensible position for Australian organisations subject to the Notifiable Data Breaches scheme.
Operational limitations and common mistakes that undermine air gapped backups
Even a well-designed air gap can fail in practice. These are the failure modes that come up most often.
Common mistakes:
- “Set and forget” media: writing a backup once and never verifying it again. Media degrades, formats become obsolete, and the restore process drifts out of sync with the current environment.
- Unsecured management consoles: leaving the backup orchestration platform accessible from the production network with standard credentials. This is the single most exploited weakness in backup infrastructure.
- Untested restore processes: assuming a backup is good because the job completed without errors. A completed backup job and a successful restore are not the same thing.
- Poor media lifecycle management: regularly migrate offline media to new media types and run full restores from migrated media; media rot and format obsolescence are real risks for long-term air-gapped archives.
- Encryption keys stored with the media: if the drive and the key are in the same location, a physical theft compromises both.
Operational limitations:
- Restore latency is real. Retrieving data from an offsite tape vault can take hours. Plan your RTO with that in mind.
- Manual processes introduce human error. Every step that relies on a person following a procedure is a potential failure point.
- Physical transport carries risk. Media can be lost, damaged, or intercepted in transit.
- Stale data is a genuine risk. If your RPO is 24 hours but your physical tape rotation runs weekly, you may lose up to seven days of data in a worst-case scenario.
Red flags for audits and tabletop exercises:
- No documented restore runbook, or a runbook that has not been updated in over 12 months.
- Backup jobs completing but no integrity verification running.
- Management console accessible with the same credentials as production systems.
- No media register or media with no labelling.
- Encryption keys stored in the same location as the media they protect.
- No record of a successful full restore test in the past 12 months.
- Physical media stored on-site only, with no offsite copy.
Retention, data sovereignty and compliance in Australia
Australian organisations designing air gapped backup systems need to account for obligations under the Privacy Act 1988, the Notifiable Data Breaches (NDB) scheme administered by the Office of the Australian Information Commissioner (OAIC), and sector-specific rules such as APRA CPS 234 for financial services and the My Health Records Act for healthcare.
The ACSC’s Essential Eight framework lists regular backups as a core mitigation strategy. The ACSC recommends that backups of important data, software, and configuration settings are performed and retained with a copy stored disconnected from the internet. Organisations should test restoration from backups as part of their cyber resilience programme and ensure backup media is protected from unauthorised access, modification, and deletion.
Practical controls to satisfy these obligations:
- Maintain a documented retention schedule that maps each dataset to its legal minimum retention period and the media on which it is stored.
- Store encryption master keys separately from backup media, with access logging and dual-control procedures for key retrieval.
- Retain audit logs of all backup creation, access, and restore events for at least the period required by your sector’s rules (commonly two to seven years).
- For data subject to Australian data sovereignty requirements, confirm that offsite vaults or cloud air gap providers store data within Australia. Cloud providers operating in Australia include options with Australian-region data residency; verify this contractually.
When to involve legal and compliance teams: before finalising your retention schedule, when selecting an offsite vault provider, and whenever a restore event occurs that may trigger NDB notification obligations. Document every decision with a rationale so auditors can follow the reasoning without needing to interview staff.
For guidance on how air gapped backups fit within a broader ACSC Essential Eight compliance programme, Techbug’s cybersecurity page covers the full control set.
What does it cost, and how long does deployment take?
Cost and timeline vary significantly by approach. The table below gives a qualitative comparison; exact figures depend on dataset size, media volumes, and whether you use in-house staff or a managed service provider.
| Approach | Primary cost drivers | Operational effort | Expected restore speed |
|---|---|---|---|
| Physical (tape offsite) | LTO hardware, media, vaulting fees, staff time | High (manual rotation, transport) | Slow (hours to days) |
| Logical (isolated vault) | Cloud storage, licensing, network segmentation | Medium (automated jobs, manual audits) | Fast (minutes to hours) |
| Hybrid (logical + physical) | Both of the above | High | Variable (fast from logical, slow from physical) |
Primary cost factors across all approaches:
- Media purchase and replacement cycles (LTO drives and cartridges, external drives)
- Secure offsite vaulting or courier fees for physical media
- Staff time for manual rotation, transport, and testing
- Encryption and key management infrastructure (HSM or cloud KMS)
- Annual or quarterly restore testing (staff time or managed service fees)
- Compliance audit documentation
Typical deployment timelines (qualitative guidance):
A small business deploying a logical air gap to a cloud vault can typically complete planning, configuration, and a pilot test within four to six weeks, assuming an existing cloud environment. A medium-sized organisation adding a physical tape component to an existing logical gap should budget eight to twelve weeks for hardware procurement, process documentation, and initial testing. An enterprise deployment with multiple sites, tiered media, and formal compliance documentation commonly runs three to six months from scoping to sign-off.
The ongoing cost of a physical air gap is dominated by staff time. If your team cannot absorb the manual overhead, a managed service that handles rotation, transport, and testing is often more cost-effective than the apparent savings of doing it in-house.
For a detailed look at how cloud backup options integrate with offline strategies, Techbug’s cloud backup guide covers hybrid architectures suited to Queensland and broader Australian SMBs.
When air gapped backup strategies have failed: lessons from real incidents
The most instructive failures are not exotic. They follow predictable patterns.
The untested tape vault. A professional services firm maintained weekly LTO tape backups stored offsite for three years. When a ransomware incident forced a full restore, the team discovered that the tape drive model used for writing had been decommissioned 18 months earlier. No compatible reader was available on-site. Recovery required sourcing a compatible drive from a third party, adding 72 hours to the outage. The lesson: media and hardware compatibility must be verified together, and a full restore test must use the actual hardware that will be available during a real incident.
The management console left exposed. A mid-sized organisation ran a logically isolated backup repository but left the backup management console accessible via the standard corporate VPN with no additional authentication. Attackers who compromised a VPN credential deleted all backup jobs and purged the repository before triggering ransomware on production systems. The air gap was logical in design but not in practice, because the management plane was reachable. Human and management interfaces are frequent weak points; securing the management console with out-of-band MFA and strict RBAC is critical.
The encryption key stored on the media. A healthcare provider encrypted backup drives correctly but stored the decryption passphrase in a text file on the same drive. When the drive was reported stolen from a courier vehicle, the data was effectively unprotected. Encryption without separate key management is security theatre.
The stale RPO mismatch. A retail business set up a physical air gap with monthly tape rotations but documented an RPO of 24 hours in their business continuity plan. During an incident, leadership expected to recover to yesterday’s data. The actual recovery point was 23 days prior. The mismatch between the documented RPO and the actual backup cadence caused significant business impact and a near-miss on NDB notification obligations.
Each of these failures was preventable with a documented runbook, a tested restore process, and a management plane hardened against the same threat model as the rest of the environment. Understanding cybersecurity fundamentals helps teams avoid treating backup security as an afterthought.
Key takeaways
Air gapped backups work because physical or logical disconnection removes the network path that ransomware and compromised credentials rely on to destroy your last line of defence.
| Point | Details |
|---|---|
| Disconnection is the core protection | An air gapped copy has no network address to target, stopping ransomware that actively hunts backup repositories. |
| Test restores, not just backup jobs | A completed backup job does not confirm a successful restore; quarterly full restore tests are the minimum for Tier 1 datasets. |
| Secure the management plane | Out-of-band MFA and strict RBAC on the backup console prevent attackers from deleting jobs after gaining network access. |
| Match RPO to rotation cadence | Your documented RPO must match your actual backup frequency; a mismatch creates compliance and recovery risk. |
| Techbug designs and operates air gapped backups | Techbug’s managed backup service covers design, encryption, testing, and emergency response for Australian SMBs. |
The gap between theory and practice in Australian SMB deployments
Most of the conversation around air gapped backups focuses on architecture: physical vs logical, tape vs cloud vault, AES-256 vs whatever the vendor defaults to. That is the easy part. The harder part, and the part that actually determines whether a business recovers, is the operational discipline that keeps the strategy working six months after deployment.
The failure mode that comes up most often in Australian SMB environments is not a technical one. It is the gradual erosion of process. A backup rotation schedule that starts rigorous and then slips because the person responsible left the business. A restore runbook that was accurate at deployment but was never updated when the application stack changed. A management console that was hardened at go-live and then had an exception added “temporarily” that was never removed.
The organisations that recover well from ransomware are not necessarily the ones with the most sophisticated architecture. They are the ones where someone owns the process, tests it regularly, and treats a failed restore test as a priority incident rather than a minor inconvenience.
For Australian SMBs, the pragmatic answer is usually a logical air gap for daily backups, combined with a monthly physical copy and a quarterly restore test. That combination covers the vast majority of threat scenarios without requiring a dedicated backup engineer. The key is making the testing non-negotiable, not optional.
The ACSC Essential Eight framework gives Australian organisations a clear benchmark for where backups fit within a broader resilience posture. Treating that benchmark as a floor rather than a ceiling is what separates organisations that recover quickly from those that spend weeks rebuilding from scratch.
Techbug protects Australian businesses with ransomware-safe backup strategies
Most Australian SMBs have some form of backup in place. Far fewer have a backup they have actually tested, encrypted correctly, and isolated from the management plane that an attacker would target first. That gap is exactly where Techbug works.
Techbug’s managed IT security services cover the full lifecycle: designing the right air gap architecture for your environment, configuring encryption and access controls, running quarterly restore tests, and responding when an incident occurs. With over 30 years of combined experience and a vendor-agnostic approach, Techbug recommends what fits your risk profile, not what a single vendor sells. The team is Brisbane-based and serves businesses across Australia, so you get local response times without the limitations of a remote-only provider.
If you want to know where your current backup strategy has gaps, the right starting point is a conversation with Techbug’s team. Contact Techbug to book an initial IT security review and find out whether your backups would actually survive a ransomware attack.
Useful sources and further reading
- CISA StopRansomware Guide: the definitive US federal guidance on ransomware defence, including backup and recovery controls. Directly applicable to Australian organisations designing resilient backup strategies.
- NCSC Ransomware-Resistant Backups: UK National Cyber Security Centre guidance on what makes a backup genuinely ransomware-resistant, covering testing, monitoring, and vendor questions.
- CISA Shields Up: operational guidance for organisations facing elevated cyber threat levels, including backup and incident response priorities.
- Microsoft Azure: Backup Plan to Protect Against Ransomware: practical technical guidance on the 3-2-1 backup rule and isolated backup architectures for cloud environments.
- IBM: What Is an Air Gap Backup?: vendor-agnostic explainer covering physical, logical, and cloud air gap categories with examples.
- OAIC Notifiable Data Breaches: Australian Information Commissioner’s guidance on NDB obligations, relevant when a restore event may trigger notification requirements.
- ACSC Essential Eight: the ACSC’s baseline mitigation strategies for Australian organisations, including the regular backups control.