What is application control and why does it matter in Australia?
Application control is the security practice of restricting software execution to a pre-approved list of applications. If a program is not on the list, it does not run. Full stop. The Australian Cyber Security Centre (ACSC) includes it as a mandatory component of the Essential Eight mitigation strategies, making it one of the most formally endorsed controls available to Australian organisations.
What makes this approach different from traditional antivirus is the logic behind it. Antivirus blocks what it knows to be bad. Application control permits only what you have explicitly approved, blocking everything else, including threats no antivirus signature has ever seen. The ACSC guidance confirms it covers executables, scripts, installers, software libraries, drivers, and compiled HTML applications, not just standard .exe files.
Key elements of a sound application control policy include:
- Allowlisting: a curated list of approved applications permitted to execute
- Cryptographic hash rules: the strongest enforcement method, using file content to generate a unique identifier
- Publisher certificate rules: combining publisher name and product name for broader coverage
- Path rules: folder-based permissions, requiring strict file system access controls
- Audit and enforce modes: audit first to observe, then enforce to block
Technologies and tools used by Australian organisations
Windows environments
Microsoft recommends App Control for Business for all new Windows deployments, given its ongoing feature development and support from the Microsoft Security Response Center. AppLocker remains available for organisations running mixed Windows environments or needing per-user policy controls, but it receives security fixes only, not new features.
App Control for Business applies policies at the device level, covering all users. Rules can be based on code-signing certificate attributes, file hash, file path, or Microsoft’s Intelligent Security Graph for reputation-based decisions. AppLocker is a practical complement for shared-device scenarios where different user groups need different restrictions.
Linux and mobile
On Linux, the File Access Policy daemon (fapolicyd) provides equivalent controls, allowing administrators to permit or deny execution based on path, hash, or MIME type. For mobile devices, application management is typically handled through Mobile Device Management (MDM) or Mobile Application Management (MAM) platforms, which enforce approved app catalogues across iOS and Android fleets.
Deployment and change management
Starting in audit mode is the standard approach. Audit mode logs what would be blocked without actually blocking it, letting your team build an accurate baseline before switching to enforce mode. Skipping this step is how organisations accidentally lock out legitimate software and disrupt operations.
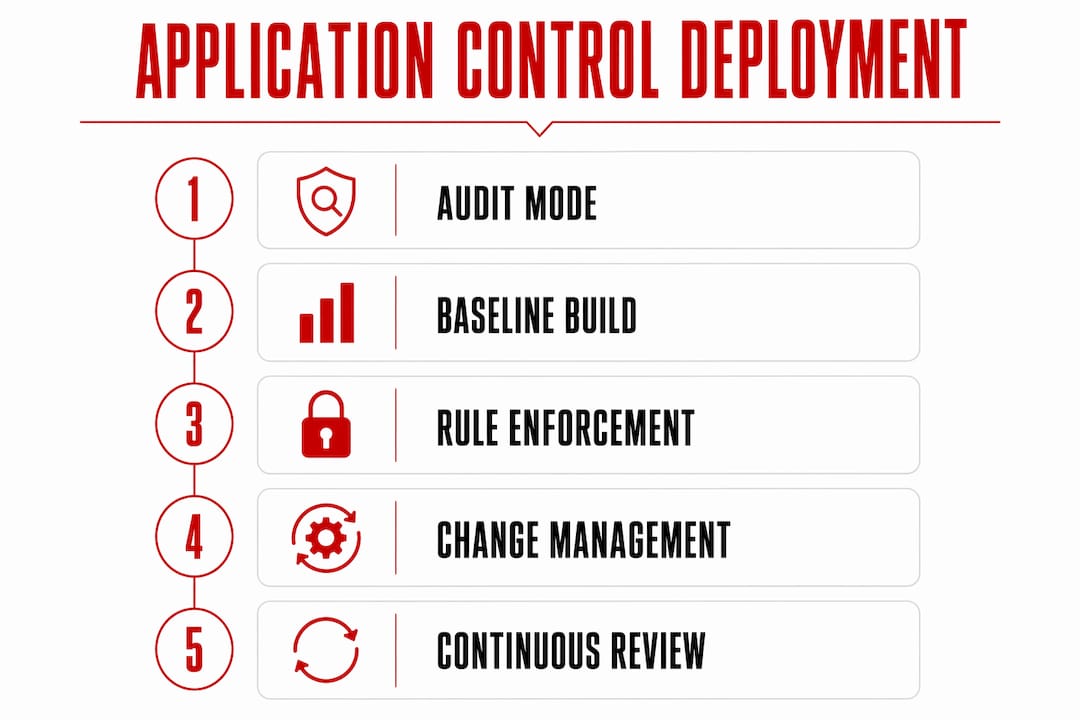
Maintaining application control rules requires a structured change management program. Every software patch, new deployment, or version update potentially changes file hashes, which means rules need updating before the change lands in production.
Pro Tip: Designate your patch management solution as a trusted updater within your application control tool. This automates hash acceptance for vendor-approved updates and cuts the administrative overhead significantly.
A persistent challenge is living-off-the-land attacks, where adversaries exploit legitimate Windows binaries like msbuild.exe to execute malicious code without triggering allowlist blocks. Mitigating this requires implementing Microsoft’s recommended application blocklist and reviewing it regularly. Policies also need to extend beyond executables to cover scripts, DLLs, and drivers to close these gaps.
Application control works alongside antivirus, not instead of it. Treat it as one layer in a broader defence strategy that includes vulnerability management and endpoint detection and response (EDR) tools.
| Approach | Best for | Key consideration |
|---|---|---|
| App Control for Business | New Windows deployments | Strongest security; requires planning |
| AppLocker | Mixed OS or per-user policies | Security fixes only; no new features |
| fapolicyd | Linux environments | Requires Linux admin expertise |
| MDM/MAM | Mobile device fleets | App catalogue management via platform |
Techbug Computer Consultants, based in Brisbane with over 30 years of combined experience, provides local implementation support for Australian SMBs navigating these technology choices.
How to select the right application control solution
Choosing the wrong tool creates either security gaps or operational chaos. Work through these steps before committing.
- Assess your environment. Catalogue every operating system, device type, and application in use. A Windows-only environment points toward App Control for Business. A mixed fleet needs a broader strategy.
- Define your risk tolerance. Organisations handling sensitive data or subject to IT compliance requirements need stricter enforcement than a small office with a stable, predictable software set.
- Evaluate rule criteria. File names and package names are not secure controls. Prioritise solutions that support cryptographic hashes and publisher certificates.
- Check integration with your existing stack. The tool should feed event logs into your SIEM or centralised logging platform. Event logs should capture file name, timestamp, and username for every blocked execution.
- Plan for ongoing maintenance. If your team cannot sustain regular rule updates, a managed service provider with local expertise, like Techbug, is worth considering for managed IT support.
- Test before enforcing. Run positive tests to confirm approved applications execute correctly, and negative tests to confirm unapproved software gets blocked. Never skip this step.
Application control in practice: Australian implementation examples
Queensland government agencies and Australian financial services firms have adopted application control as a baseline control, driven largely by the ACSC Essential Eight compliance requirements. The pattern across successful implementations is consistent: audit mode first, enforce mode only after thorough testing, and a formal change process for every software update.
A common scenario in Australian SMBs involves a business running a stable suite of line-of-business applications, where managing digital presence for SMB growth plays a critical role alongside application control. After deploying App Control for Business in audit mode for four weeks, the IT team identifies a handful of shadow IT tools staff had been running without approval. Those tools get formally reviewed, approved or removed, and the policy moves to enforce mode with a clean baseline. The security benefit is immediate: unknown executables are blocked, and every blocked attempt generates a log entry with the file name, timestamp, and user account involved.
For businesses without dedicated security staff, partnering with a local provider removes the guesswork. Techbug’s cybersecurity consulting services cover Essential Eight implementation, including application control deployment and ongoing policy maintenance, tailored to the specific software environments Queensland businesses actually run.
Key takeaways
Application control is the single most effective technical control for blocking unauthorised software execution, and the ACSC mandates it within the Essential Eight for good reason.
| Point | Details |
|---|---|
| Start in audit mode | Build a trusted application baseline before switching to enforce mode to avoid blocking legitimate software. |
| Use strong rule criteria | Cryptographic hashes and publisher certificates are secure; file names and package names are not. |
| Extend beyond executables | Policies must cover scripts, installers, DLLs, and drivers to block living-off-the-land attacks. |
| Pair with antivirus | Application control complements antivirus within a layered defence; it does not replace it. |
| Maintain rules continuously | A change management program is required to keep allowlists current as software updates and patches arrive. |
Techbug’s team brings IT security expertise built over more than 30 years of supporting Australian businesses. Whether you are starting from scratch or tightening an existing policy, Techbug provides the local knowledge and hands-on support to get application control working without disrupting your operations.