
A BCP business continuity plan is a documented strategy that prepares your business to maintain critical functions and recover quickly when disruptions strike. For Queensland small and medium businesses, the stakes are real: cyberattacks, floods, supply chain failures, and power outages can all halt operations without warning. A well-built plan, aligned with standards like ISO 22301:2019, defines your Recovery Time Objective (RTO) and Recovery Point Objective (RPO), assigns clear roles, and keeps your business moving when conditions are anything but normal. Operational resilience, not just compliance, is the true measure of a plan’s success.
What are the essential components of a BCP business continuity plan?
A business continuity plan covers far more than IT recovery. It addresses every part of your business that must keep functioning during a disruption, from your people and premises to your suppliers and customers.
The core components every plan needs:
- Risk assessment. Identify the threats most likely to affect your business. For Queensland businesses, this includes cyclones, flooding, ransomware attacks, and supply chain failures. 42% of cyberattacks target small businesses, making cyber threats a top priority in any risk register.
- Business Impact Analysis (BIA). The BIA identifies which functions are critical and what happens if they stop. It sets your RTO (how quickly you must restore a function) and RPO (how much data loss is acceptable). Skipping the BIA before selecting recovery strategies is one of the most common and costly mistakes SMEs make.
- Recovery strategies. These cover people (remote work, cross-training), facilities (alternate sites), technology (cloud backups, failover systems), and communications.
- Roles and responsibilities. Every plan needs a named owner and a clear chain of command. Governance gaps are the leading cause of plans that look good on paper but fail in practice.
- Communication plan. Your plan must cover internal notifications, leadership reporting, and customer communications. Clear communication reduces confusion during disruptions and speeds up recovery.
- Testing and maintenance procedures. A plan that has never been tested is a plan that will fail when you need it most. Schedule exercises at least twice a year and update the plan after every major change to your business.
Each component builds on the last. Miss one, and you create a gap that a real incident will find.
How does a business continuity plan differ from disaster recovery?
Business continuity and disaster recovery are related but distinct. Confusing them creates dangerous gaps in your preparedness.
A BCP covers the whole business: people, processes, facilities, communications, and technology. It answers the question, “How do we keep operating?” Disaster recovery (DR) is a specialised subset focused on restoring IT systems and data after a technical failure. DR answers the question, “How do we get our systems back online?”
Think of it this way: your BCP is the master plan, and your DR plan is one chapter within it. A business continuity strategy without a solid DR component leaves your technology recovery undefined. A DR plan without a BCP leaves your people, customers, and operations without direction.
The real-world risk of mixing these up is significant. A business that treats its DR plan as its entire BCP will restore its servers but have no plan for staff working from home, no customer communication protocol, and no process for managing suppliers during the outage. Misalignment between BCP and DR leads to false confidence and costly gaps.
Pro Tip: Link your IT disaster recovery runbooks directly to your BCP’s recovery objectives. If your BCP sets a four-hour RTO for your order management system, your DR runbook must demonstrate it can meet that target.
What practical steps should SMEs follow to create an effective BCP?
Building a business continuity plan does not require a large team or a big budget. The UNDRR recommends a tiered approach for SMEs, using templates that scale from basic to advanced as your business matures. Start simple, then build.
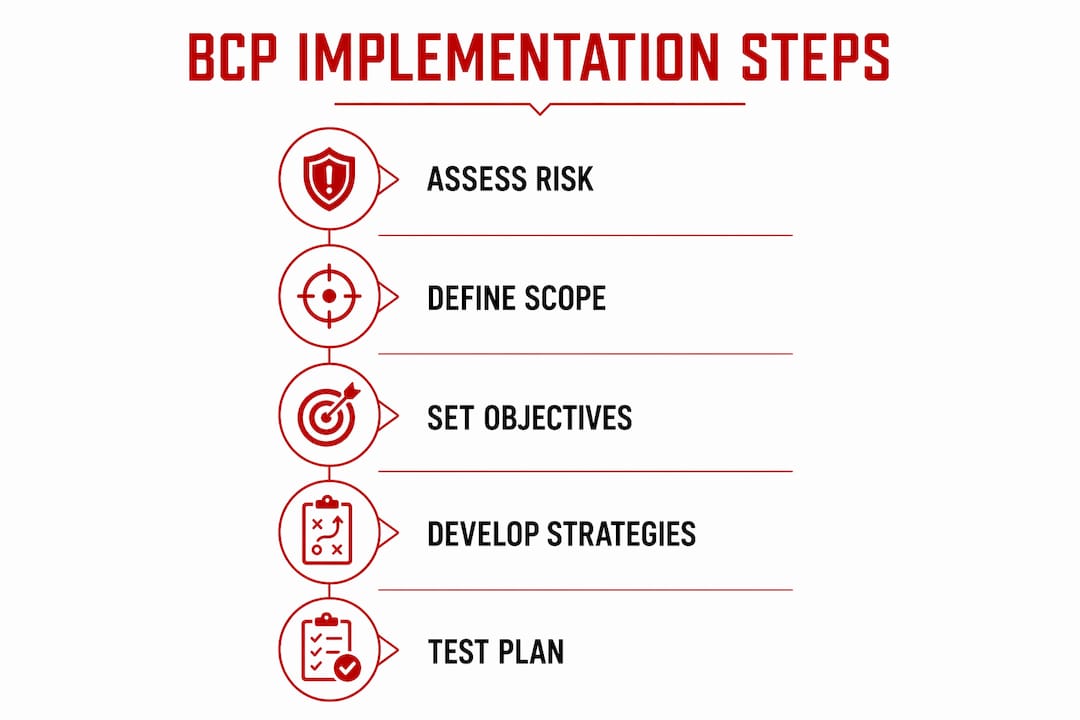
Step-by-step BCP implementation guide
-
Define scope and secure leadership commitment. Decide which parts of your business the plan covers. Get your owner or senior leadership on record as sponsors. A plan without executive backing rarely gets the resources or attention it needs.
-
Conduct your risk assessment. List every credible threat: cyberattacks, natural disasters, key staff illness, supplier failure, and infrastructure outages. Rate each by likelihood and impact. Queensland businesses should weight weather events and cyber threats heavily.
-
Complete your Business Impact Analysis. For each critical function, document what happens if it stops for one hour, one day, or one week. Set your RTO and RPO for each function. ISO 22301 compliance requires this step before you select any recovery strategy. Setting strategies before you know your recovery targets is a strategic mistake.
-
Develop recovery strategies. Match each critical function to a recovery approach. For technology, this means cloud backups and failover systems. For people, this means cross-training and remote work capability. For facilities, this means identifying an alternate work location.
-
Document the plan clearly. Write procedures that any staff member can follow under pressure. Avoid jargon. Include contact lists, decision trees, and escalation paths. Keep the document accessible offline as well as online.
-
Align your BCP with IT disaster recovery. Your IT recovery runbooks must reflect the RTO and RPO targets set in your BIA. Validated recovery targets prevent the false confidence that comes from untested assumptions.
-
Train your team and test the plan. Run a tabletop exercise first: walk your team through a scenario in a meeting room. Then progress to simulations and functional recovery tests. Testing multiple times per year produces faster recovery, lower costs, and less reputational damage than annual reviews alone.
-
Set a maintenance schedule. Review your plan every six months and after any major change: new systems, new staff, new suppliers, or a significant incident. A plan that is 12 months old without a review is already out of date.
Pro Tip: Use a tiered BCP template to match your current maturity level. A one-page plan is better than no plan. Build complexity as your business grows and your team gains confidence.
The following table shows how recovery objectives map to business functions for a typical Queensland SME:
| Business function | RTO target | RPO target |
|---|---|---|
| Customer order processing | 4 hours | 1 hour |
| Financial transactions | 2 hours | 30 minutes |
| Staff communications | 1 hour | N/A |
| Supplier management | 24 hours | 4 hours |
| Website and online sales | 8 hours | 2 hours |
These targets are examples. Your BIA will produce the specific numbers that reflect your actual business risk.
What are best practices for maintaining and testing your plan?
A business continuity plan is a living document. Plans become stale within 6–12 months without realistic, scenario-based testing. Most SMEs write a plan and file it. That is the single biggest mistake in business continuity management.
The most effective testing programme uses three formats:
- Tabletop exercises. Gather your team and walk through a scenario verbally. No systems are activated. The goal is to identify gaps in decision-making and communication.
- Simulation exercises. Replicate conditions more closely. Staff act out their roles without fully activating recovery systems. This builds the muscle memory that documentation alone cannot create.
- Functional recovery tests. Fully activate recovery procedures for one or more functions. Restore data from backups. Switch to alternate systems. Measure actual RTO and RPO against your targets.
“Auditors focus more on tested plans than paperwork. Evidence of improvements made after testing is critical for ISO 22301 compliance. A plan that has never been exercised is a plan that has never been proven.”
Use the Plan-Do-Check-Act (PDCA) cycle to drive continuous improvement. After every test, document what worked, what failed, and what changed. Track key risk indicators (KRIs) such as the number of unresolved gaps from previous tests. ISO 22301:2019 Clause 8.5 mandates regular exercises against realistic scenarios tailored to your risk profile. Meeting that standard is not just about compliance. It is about knowing your plan actually works.
How can SMEs align their BCP with ISO 22301:2019?
ISO 22301:2019 is the international standard for business continuity management systems. Aligning your plan with it gives you a credible, auditable framework and strengthens your position with regulators, insurers, and major clients.
The standard follows a BCM lifecycle that maps directly to the steps covered above. The table below shows how key ISO 22301 clauses align with BCP activities for SMEs:
| ISO 22301 clause | BCP activity | SME focus |
|---|---|---|
| Clause 4: Context | Scope definition and stakeholder needs | Define what the plan covers |
| Clause 6: Planning | Risk assessment and BIA | Set RTO/RPO targets |
| Clause 8.3: BIA | Critical activity identification | Prioritise recovery order |
| Clause 8.4: Strategy | Recovery strategy development | People, tech, facilities |
| Clause 8.5: Testing | Exercises and simulations | Build and test muscle memory |
| Clause 10: Improvement | PDCA and post-test reviews | Close gaps continuously |
You do not need full certification to benefit from ISO 22301 alignment. The UNDRR’s tiered templates let SMEs adopt the standard’s structure progressively, starting with the clauses most relevant to their size and risk profile. The key is to document your BIA, risk assessments, and testing records. These are the evidence auditors and insurers look for, and they are the foundation of a plan that holds up under pressure.
Key takeaways
A BCP business continuity plan succeeds when it is built on a thorough BIA, aligned with measurable recovery objectives, tested regularly, and owned by accountable leaders across the business.
| Point | Details |
|---|---|
| Start with the BIA | Set RTO and RPO targets before selecting any recovery strategy. |
| Cover the whole business | A BCP addresses people, facilities, communications, and technology, not just IT. |
| Test multiple times per year | Organisations that test regularly recover faster and at lower cost than those that review annually. |
| Align BCP and DR | Link IT disaster recovery runbooks to BCP recovery objectives to prevent gaps. |
| Use ISO 22301 as your framework | Align with the standard progressively using tiered templates suited to your business size. |
Why most SME continuity plans fail before they are ever needed
Working with Queensland businesses over the years, I have seen the same pattern repeat. A business owner invests time in writing a continuity plan, files it, and considers the job done. Then a ransomware attack or a flood hits, and the plan is either out of date, untested, or sitting on a server that is no longer accessible.
The uncomfortable truth is that most SME continuity plans are written for the feeling of security, not for actual use. They list recovery steps that have never been practised, assign roles to people who do not know they have them, and set RTO targets that have never been validated against real IT recovery capability.
The businesses I have seen recover well from serious disruptions share one trait: they treated their plan as a training programme, not a document. They ran tabletop exercises. They tested their backups. They made sure every person in the business knew their role before an incident, not during one. That preparation is what operational resilience actually looks like in practice.
My advice to any Queensland SME owner is this: do not wait for a perfect plan. Start with a one-page BIA, set two or three recovery objectives, and run a 30-minute tabletop exercise with your team this month. A simple, tested plan beats a detailed, untested one every time.
— Ru
How Techbug supports your business continuity planning
Building a continuity plan is one thing. Having the IT infrastructure to back it up is another.
Techbug, based in Brisbane, works with Queensland SMEs to align their IT capabilities with their business continuity requirements. With over 30 years of combined experience in managed IT support and cybersecurity, Techbug delivers ransomware-safe backups, proactive monitoring, and cloud solutions that directly support your RTO and RPO targets. Whether you are starting your first BCP or strengthening an existing one, Techbug’s vendor-agnostic approach means you get the right technology for your business, not a locked-in solution. Talk to the team about how your IT setup measures up against your continuity objectives.
FAQ
What does BCP stand for in business?
BCP stands for Business Continuity Plan. It is a documented strategy that defines how a business will maintain critical functions and recover from disruptions such as cyberattacks, natural disasters, or supply chain failures.
What is the difference between RTO and RPO?
RTO (Recovery Time Objective) is the maximum time your business can tolerate a function being offline. RPO (Recovery Point Objective) is the maximum amount of data loss your business can accept, measured in time. Both are set during the Business Impact Analysis.
How often should a business continuity plan be tested?
Organisations that test their plans multiple times per year recover faster and at lower cost than those that conduct only annual reviews. ISO 22301:2019 Clause 8.5 requires regular exercises against realistic scenarios tailored to your risk profile.
Is ISO 22301 certification required for SMEs?
Certification is not required, but aligning with ISO 22301:2019 gives SMEs a credible, auditable framework. The UNDRR offers tiered templates that let smaller businesses adopt the standard’s structure progressively without full certification.
How is a BCP different from a disaster recovery plan?
A BCP covers the entire business, including people, processes, facilities, and communications. A disaster recovery plan is a specialised IT-focused subset that addresses restoring systems and data. Both are needed, and they must be aligned to avoid gaps.