
Secure your business email now by enforcing multi-factor authentication, publishing and enforcing SPF/DKIM/DMARC, adding a specialised anti-phishing layer on top of your existing platform, and running regular staff phishing simulations. Those five controls, applied in order, block the vast majority of email-based attacks targeting Australian small and medium businesses.
The single most important thing you can do today: Turn on MFA for every mailbox. MFA is the most effective single control against unauthorised account access, and it takes under an hour to enforce across Microsoft 365 or Google Workspace.
Do these right now:
- Enable MFA on every account, starting with admin and finance roles
- Check your DMARC record is at least at
p=nonewith a reporting address configured - Force a password reset on any account that has shown unusual login activity
- Pause any automated payment or supplier-change processes until you confirm no active compromise
- Audit mailbox forwarding rules for anything you did not set up yourself
Medium-term (next 30–90 days):
- Move DMARC from
p=nonetop=quarantineorp=rejectonce you have reviewed reports - Deploy a dedicated anti-phishing layer on top of your Microsoft 365 or Google Workspace plan
- Run your first role-based phishing simulation
- Implement DLP policies for regulated or sensitive communications
Table of Contents
- Why business email security matters for Australian SMBs
- How attackers target your inbox: the main threats to know
- What controls to implement first, and in what order
- How to configure Microsoft 365 and Google Workspace securely
- What to do in the first hours after a compromise
- What email security upgrades typically cost and how long they take
- How to choose a managed email security provider: questions to ask
- How Techbug implements email security for Australian SMBs
- Key takeaways
- The case for layered defences and human-centred controls
- Techbug’s email security services for Australian businesses
- Authoritative sources and further reading
Why business email security matters for Australian SMBs
Email security is the combination of controls, protocols, and policies that protect your organisation’s email accounts and communications from unauthorised access, data loss, and abuse. That covers everything from authentication records in your DNS to how your staff recognise a suspicious message.
For Australian small and medium businesses, the stakes are concrete. Business email compromise (BEC) is one of the costliest cyber threats in the country. The Australian Cyber Security Centre (ACSC) specifically calls out BEC as a priority threat, where attackers impersonate executives or suppliers to redirect payments or extract sensitive data. A single successful BEC incident can cost a business tens of thousands of dollars, and the reputational damage with suppliers and customers often outlasts the financial hit.
Cyberattacks often target small businesses, yet most SMBs still rely on default platform settings and annual security awareness sessions that do not reflect how modern attacks actually work.
There are also regulatory consequences. Under the Privacy Act 1988, Australian businesses that hold personal information have notification obligations when a data breach is likely to cause serious harm. The Office of the Australian Information Commissioner (OAIC) handles these notifications, and a compromised email account that exposes customer data can trigger that process.
The deliverability angle is just as real. SPF, DKIM, and DMARC enforcement are now foundational requirements for inbox placement, not just security hygiene. A damaged sender reputation from a compromised account or poor list hygiene can block your legitimate business mail from reaching customers entirely.
How attackers target your inbox: the main threats to know
Most email attacks succeed not because they are technically sophisticated, but because they are well-timed and plausible. Understanding the mechanics helps you prioritise the right controls.
Phishing and spear-phishing are the most common entry points. A generic phishing email casts a wide net; spear-phishing is targeted, using your name, your supplier’s name, or a recent invoice number to look credible. AI-generated phishing messages are now common, and they evade legacy signature-based filters because they contain no malicious links or attachments at the point of delivery.
Business email compromise (BEC) is the high-value variant. An attacker either compromises a real email account or spoofs one convincingly, then impersonates a CEO, CFO, or supplier to request an urgent payment or a change to banking details. The message often arrives on a Friday afternoon, referencing a real project, with a tone that discourages verification.
Account takeover happens when credentials are stolen via phishing or credential-stuffing attacks against reused passwords. Once inside, attackers set up silent forwarding rules, monitor communications for payment opportunities, and sometimes sit undetected for weeks.
Domain spoofing and lookalike domains let attackers send mail that appears to come from your domain or a near-identical one (think techbug.com.au versus techbug-support.com.au). Without DMARC enforcement, your domain can be spoofed by anyone.
Malicious attachments and links remain a reliable delivery mechanism for malware and ransomware. The payload is often a macro-enabled document or a link that is clean at delivery but weaponised hours later, after it has passed your initial scan.
Supply-chain impersonation targets the trust you have with known suppliers. Attackers compromise a supplier’s account or spoof their domain, then insert themselves into an existing email thread to redirect a payment.
Watch for these signals in your inbox: unexpected urgency around payments or credential changes, sender addresses that are one character off, links where the displayed URL does not match the destination, and requests that bypass your normal approval process. These are not edge cases — they are the standard playbook.
What controls to implement first, and in what order
A practical email security checklist does not treat all controls as equal. Here is a prioritised sequence based on impact, cost, and how quickly you can deploy each one.
1. Enforce multi-factor authentication across every account
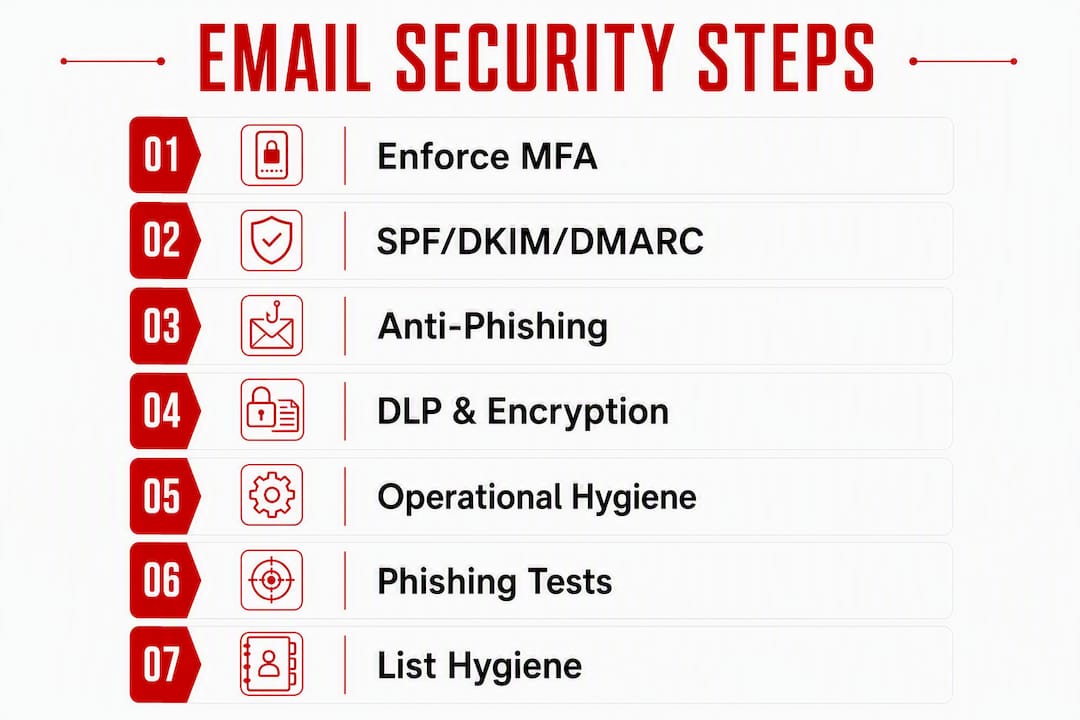
MFA is the fastest, cheapest, and highest-impact control available. Enforce it organisation-wide, not just for admins. Use an authenticator app (Microsoft Authenticator, Google Authenticator) rather than SMS where possible, since SMS codes can be intercepted. Set conditional access policies so that logins from unfamiliar locations or devices trigger additional verification.
2. Publish and enforce SPF, DKIM, and DMARC
These three DNS records work together to prove your mail is legitimate and to instruct receiving servers what to do with mail that fails authentication.
- SPF lists the servers authorised to send mail on behalf of your domain
- DKIM adds a cryptographic signature to outgoing messages that receivers can verify
- DMARC ties SPF and DKIM together and tells receivers whether to monitor, quarantine, or reject unauthenticated mail
Start with p=none and a reporting address so you can see what is sending mail on your behalf before you enforce. Move to p=quarantine once you have reviewed two to four weeks of reports, then to p=reject when you are confident all legitimate senders are authorised. Maintaining SPF/DKIM/DMARC alignment is ongoing work: adding a new CRM, marketing platform, or SaaS tool often breaks alignment and requires a DNS update.
Pro Tip: Schedule a quarterly DNS review in your calendar and tie it to your change management process. Any time a new SaaS tool is onboarded, check whether it sends mail on your behalf and update your SPF record before it goes live.
3. Add a dedicated anti-phishing layer
Microsoft 365 and Google Workspace provide baseline filtering, but modern attacks change after delivery and need continuous monitoring and behaviour-based detection that native controls do not provide. A specialist layer such as Proofpoint or Trend Micro sits on top of your existing platform and adds post-delivery scanning, link rewriting, and behavioural anomaly detection. Techbug deploys these as part of its managed security services for Australian SMBs.
4. Apply data loss prevention and encryption policies
Configure DLP policies to flag or block outbound mail containing tax file numbers, credit card numbers, or other regulated data. Enforce TLS for outbound connections so mail in transit is encrypted. For genuinely sensitive regulated communications, S/MIME or PGP end-to-end encryption provides a stronger guarantee than transport-level TLS alone.
5. Operational hygiene: patching, least privilege, and backups
Keep your email client and operating system patched. Apply least-privilege principles so that a compromised account cannot access every mailbox in the organisation. Enable mailbox auditing so you have a log of login events, forwarding rule changes, and delegation changes. Maintain automated, immutable backups of your email data so you can restore from a point before a compromise without paying a ransom.
6. Run regular, role-based phishing simulations
Periodic, role-based phishing simulations are more effective than annual classroom training. Finance staff should receive simulations that mimic BEC and invoice fraud. Customer-facing staff should see credential-harvesting scenarios. Keep training modules short (five to ten minutes) and run them quarterly. The goal is to build a habit of verification, not to catch people out.
7. List hygiene and sender reputation maintenance
Stale email lists increase bounce rates and damage your sender reputation, which affects inbox placement for all your business mail. Validate addresses at capture and run periodic batch verification. A damaged reputation from a compromised account or a poorly managed campaign can block legitimate business mail from reaching customers entirely.
How to configure Microsoft 365 and Google Workspace securely
Platform defaults are not security defaults. Both Microsoft 365 and Google Workspace ship with settings that prioritise ease of use over protection, and most SMBs never change them.
Microsoft 365 configuration checklist
- Enable organisation-wide MFA via the Microsoft 365 admin centre; use Conditional Access policies rather than legacy per-user MFA where your licence allows
- Turn on mailbox auditing for all users (it is not enabled by default on older tenants)
- Enable Microsoft Defender for Office 365 Safe Links and Safe Attachments if your licence includes them; these rewrite URLs at click time and detonate attachments in a sandbox
- Configure mail flow rules to block common attachment types used in malware delivery (.exe, .vbs, .js, macro-enabled Office files)
- Set your DMARC, DKIM, and SPF records in your DNS and verify alignment using Microsoft’s DMARC reporting or a third-party tool
- Disable automatic external email forwarding at the tenant level; individual users should not be able to silently forward all mail to an external address
- Review and restrict OAuth app permissions so third-party apps cannot access mailboxes without admin approval
- Check Microsoft’s own security documentation for current recommended baselines, as settings and licence tiers change
Google Workspace configuration checklist
- Enforce 2-step verification for all users from the Admin console; set it as mandatory rather than optional
- Configure DKIM signing in the Admin console under Apps > Google Workspace > Gmail > Authenticate email
- Enable the spam and phishing filters under Gmail’s advanced settings and review the pre-delivery message scanning options
- Set up context-aware access policies to restrict logins from unmanaged or high-risk devices
- Review SMTP relay settings to confirm only authorised services can send mail through your domain
- Enable Google Workspace alerting for suspicious login activity, admin changes, and forwarding rule creation
- Apply data regions and DLP rules for regulated data under the compliance settings
Adding a third-party anti-phishing layer
Both platforms support adding a specialist security layer without changing your MX records, using API-based integration. This approach means your mail still flows through Microsoft or Google’s infrastructure, but the specialist tool scans delivered messages, rewrites links, and can retract messages post-delivery if a threat is identified later. Techbug’s IT security services include deployment and ongoing management of these layers for Australian SMBs.
Platform governance note: Assign a named owner for security configuration changes in both platforms. Record all changes in a simple change log with a date, the change made, and who approved it. This is the minimum you need to diagnose a deliverability or security issue quickly.
What to do in the first hours after a compromise
Speed matters. The longer a compromised account stays active, the more damage an attacker can do and the harder forensics becomes.
- Remove any forwarding rules or inbox rules — the attacker may have created. In Microsoft 365, check both the Outlook web client rules and the Exchange admin centre transport rules. In Google Workspace, check Gmail settings and the Admin console for delegation changes.
- Notify affected parties — If customer or supplier data was exposed, or if fraudulent payment instructions were sent from the account, notify those parties promptly. Under the Notifiable Data Breaches scheme, if the breach is likely to cause serious harm, you must notify the OAIC and affected individuals.
- Report to the ACSC — The Australian Cyber Security Centre provides incident reporting for Australian organisations and can offer guidance on containment and recovery. Report at cyber.gov.au.
If you do not have an incident response plan in place before a compromise occurs, the first hours will be chaotic. Document the steps above now, assign roles, and store the plan somewhere accessible outside your email system — because if your email is compromised, you may not be able to reach it.
For businesses without in-house IT capability, Techbug’s emergency response team is available to contain, investigate, and recover from email compromises. See cloud backup and recovery options for immutable backup configurations that support fast recovery.
What email security upgrades typically cost and how long they take
Cost and timeline vary significantly depending on what you already have in place, your platform, and whether you manage the work in-house or engage a provider.
What you can do in one day (low cost):
- Enable MFA across all accounts
- Publish a DMARC monitoring record (
p=none) if none exists - Audit and remove suspicious forwarding rules
- Force password resets on high-risk accounts
One to four weeks (low to medium cost):
- Review DMARC reports and begin moving toward
p=quarantine - Configure Safe Links and Safe Attachments in Microsoft 365 Defender
- Enable mailbox auditing and set up alerting for suspicious activity
- Run a baseline phishing simulation to establish a benchmark
One to three months (medium cost):
- Deploy a dedicated anti-phishing layer (Proofpoint, Trend Micro, or equivalent)
- Implement DLP policies for regulated data
- Complete DMARC enforcement (
p=reject) after confirming all legitimate senders are authorised - Deliver role-based phishing simulation training for finance, admin, and executive staff
Three to six months (medium to higher cost):
- Operationalise continuous monitoring and alerting
- Integrate email security controls with endpoint protection and SIEM logging
- Establish quarterly DNS and authentication review cycles
- Develop and test a documented incident response plan
| Control category | Cost band | Speed to deploy | Maintenance level |
|---|---|---|---|
| MFA enforcement | Low | 1 day | Low (periodic review) |
| SPF/DKIM/DMARC setup | Low–medium | 1–4 weeks | Medium (quarterly DNS review) |
| Anti-phishing layer | Medium | 2–6 weeks | Medium (policy tuning) |
| DLP policies | Medium | 4–8 weeks | Medium (rule updates) |
| Managed monitoring | Medium–high | 4–12 weeks | Low (provider-managed) |
| Staff phishing simulations | Low–medium | 2–4 weeks to first run | Medium (quarterly cadence) |
| Immutable backups | Low–medium | 1–2 weeks | Low (automated) |
Ongoing costs include DNS management, phishing simulation platform licences, anti-phishing layer subscriptions, and the staff time (or provider fees) for quarterly reviews. For most Australian SMBs, a co-managed model where a provider handles monitoring and DNS upkeep while internal staff manage day-to-day operations offers the best balance of cost and coverage.
How to choose a managed email security provider: questions to ask
Choosing a provider is not just about price. The wrong provider can leave gaps that a well-resourced attacker will find.
Questions to ask any prospective provider:
- Can you demonstrate hands-on experience configuring Microsoft 365 and Google Workspace security settings, including DMARC enforcement and Defender for Office 365?
- What is your incident response SLA? How quickly will you respond to a suspected compromise, and what does your containment process look like?
- Do you provide immutable backups, and can you demonstrate a restore from a point before a compromise?
- How do you handle DMARC reporting and SPF/DKIM alignment reviews when we add new SaaS tools?
- Do you offer role-based phishing simulations, and how do you tailor scenarios to our industry and staff roles?
- Are you aligned with the ACSC Essential Eight framework? Can you show us where our current environment sits against that baseline?
Red flags to watch for:
- Vague SLAs with no defined response times or escalation paths
- No forensic reporting capability (you need logs and evidence, not just a clean-up)
- No local Australian support or after-hours emergency contact
- Absence of immutable backups in their service offering
- A single-vendor lock-in approach with no explanation of why that vendor is the right fit for your environment
Who should manage what:
For most SMBs, a co-managed model works well. Your internal staff handle day-to-day operations and user requests; the provider owns security monitoring, DNS and authentication upkeep, incident response, and quarterly reviews. Full managed is appropriate when you have no internal IT capability at all. Pure in-house management is viable only if you have a dedicated IT person with current security training and the time to stay across threat developments.
What to request as evidence:
Ask for a sample incident response runbook, an anonymised example of a remediation engagement, and a mapping of their services to the ACSC Essential Eight. A provider who cannot produce these is telling you something important about their maturity.
Pro Tip: Before signing any managed services agreement, ask the provider to run a DMARC report review on your domain during the sales process. It takes them 20 minutes and immediately shows whether they know what they are doing.
How Techbug implements email security for Australian SMBs
When a business contacts Techbug after a suspected email compromise, the process follows a clear sequence. First, the environment is assessed: mailbox audit logs are reviewed, forwarding rules are checked, DMARC and SPF records are validated, and active sessions are examined for anomalies. Priority fixes are applied within the first engagement, typically MFA enforcement, session revocation, and removal of malicious rules. Platform hardening follows, covering the Microsoft 365 or Google Workspace configuration checklist described above. Staff training is delivered within the first month, tailored to the roles most targeted in the incident. Ongoing monitoring and quarterly reporting keep the environment current as the threat landscape and the business’s SaaS stack evolve.
Techbug’s vendor-agnostic approach means the right tool is selected for the environment, not the one that pays the highest referral margin. For businesses that need Trend Micro-based protection, Techbug is a Trend Micro partner and can deploy and manage that layer directly. For businesses already on Microsoft 365, the focus is on maximising what the existing licence provides before adding cost.
Techbug’s email security service flow:
- Initial assessment: audit of current authentication records, platform configuration, and access controls
- Priority fixes: MFA enforcement, DMARC monitoring setup, forwarding rule audit, privileged account review
- Platform hardening: full Microsoft 365 or Google Workspace configuration review and remediation
- Anti-phishing layer deployment: selection and configuration of a specialist tool suited to the environment
- Staff training: role-based phishing simulations and short micro-training modules
- Ongoing monitoring: continuous alerting, quarterly DNS and authentication reviews, and incident response on call
Techbug has over 30 years of combined experience in IT support and cybersecurity for Australian businesses. The emergency response team is available when a compromise cannot wait for a scheduled appointment.
For an assessment of your current email security posture, visit Techbug’s IT security services page.
Key takeaways
Effective business email security requires MFA, enforced DMARC, a specialist anti-phishing layer, and regular staff simulations — applied in that order, with quarterly maintenance to keep authentication records aligned as your SaaS environment changes.
| Point | Details |
|---|---|
| MFA is the highest-impact first step | Enforce MFA on every account today; it stops the majority of account takeover attempts. |
| DMARC enforcement protects your domain | Move from p=none to p=reject progressively; quarterly DNS reviews prevent alignment failures when new tools are added. |
| Native platform controls are not enough | Microsoft 365 and Google Workspace need a specialist anti-phishing layer to catch AI-enhanced and post-delivery threats. |
| Human error is the primary attack vector | Role-based phishing simulations run quarterly outperform annual training and build lasting verification habits. |
| Techbug provides end-to-end email security | From DMARC setup and platform hardening to incident response and staff training, Techbug covers the full checklist for Australian SMBs. |
30-day checklist: Enable MFA organisation-wide, publish a DMARC monitoring record, audit forwarding rules, force password resets on suspicious accounts, and run a baseline phishing simulation.
90-day checklist: Move DMARC to p=quarantine or p=reject, deploy a dedicated anti-phishing layer, deliver role-based phishing training for finance and admin staff, and implement DLP policies for regulated communications.
180-day checklist: Operationalise continuous monitoring and alerting, complete the first quarterly SPF/DKIM/DMARC review, integrate email security with endpoint protection, and test your documented incident response plan.
The case for layered defences and human-centred controls
The conventional wisdom in email security spending is to buy a better filter. Buy a smarter gateway, a more expensive licence tier, a tool with a more impressive threat-intelligence feed. The technology matters, but it is not where most Australian SMBs are losing.
They are losing because a staff member in accounts payable received a well-crafted invoice from what looked like a known supplier, and nobody had ever shown them what that kind of fraud looks like in practice. The filter passed it because it contained no malicious link or attachment at delivery. The DMARC record was at p=none because nobody had reviewed the reports since it was set up two years ago. The attacker had been monitoring the mailbox for three weeks before making a move.
Technology without training is a perimeter with an unlocked door. Training without technology is a door with no lock at all. The businesses that come through email attacks with minimal damage are the ones that have both, maintained consistently, with someone accountable for the quarterly review that nobody else wants to do.
Vendor-agnostic recommendations matter here too. The right anti-phishing layer for a 15-person business on Microsoft 365 Business Basic is not the same as the right layer for a 200-person firm on E3. Matching the control to the environment, rather than defaulting to the most expensive option or the one the reseller prefers, is how SMBs get genuine protection without overspending.
Techbug’s email security services for Australian businesses
Most Australian SMBs are one well-timed phishing email away from a BEC incident that costs more to recover from than a year of proper security management. Techbug’s managed IT security services give you the full stack without the overhead of building it in-house: DMARC and SPF/DKIM setup and ongoing management, anti-phishing layer deployment (including Trend Micro), Microsoft 365 and Google Workspace hardening, role-based phishing simulations, immutable backups, and emergency incident response when something goes wrong.
Techbug is based in Brisbane and works with businesses across Australia. The vendor-agnostic approach means you get the right tool for your environment, not the one that suits a reseller’s margin. With over 30 years of combined experience, the team has seen the full range of email-based attacks and knows what actually stops them at the SMB level.
To get a plain-language assessment of your current email security posture and a prioritised list of what to fix first, contact Techbug for an IT security assessment.
Authoritative sources and further reading
- ACSC — Preventing business email compromise: The Australian Cyber Security Centre’s primary guidance on BEC, including how attacks work and what controls to apply. The authoritative Australian source for incident reporting and response guidance.
- Microsoft — What is email security?: Microsoft’s overview of email security concepts and recommended controls for Microsoft 365 environments, including Defender for Office 365 configuration guidance.
- OAIC — Notifiable Data Breaches: The Office of the Australian Information Commissioner’s guidance on notification obligations under the Privacy Act 1988, relevant when a compromised email account exposes personal information.
- Techbug — IT security services: Techbug’s managed IT security services for Australian SMBs, covering email security assessments, DMARC management, anti-phishing deployment, and incident response.