
A solid business wifi setup starts with one decision: choose a cloud-managed, wired-backhaul architecture with VLAN segmentation and WPA3 or 802.1X authentication for staff. Everything else follows from that. Before you order a single access point, do three things: audit your peak concurrent users and the apps they run, run a wired speed test from your ISP gateway, and book a site survey. If your office has more than 15 staff, multiple floors, VoIP, POS terminals, or any PCI compliance requirement, hire a professional. The ACMA governs spectrum use in Australia, and your installation must comply with its equipment standards. Target a minimum RSSI of −67 dBm at every client device for reliable voice and video. Techbug can handle the whole process for Australian businesses that want it done right the first time.
Immediate actions:
- Audit your user count, device types, and latency-sensitive apps (VoIP, video conferencing, POS)
- Test your wired ISP speed at the gateway before assuming the problem is Wi-Fi
- Schedule a site survey, predictive or active, before purchasing hardware
- DIY is reasonable for a single open-plan floor with fewer than 15 staff and no PCI or VoIP requirements; hire a professional for anything more complex
Table of Contents
- Why business Wi-Fi differs from home Wi-Fi
- How to plan your business wifi setup: audit users, apps and space
- How to select your ISP, gateway and business-grade hardware
- Best practices for access-point placement and installation
- Network security configuration to apply during setup
- How to test, validate and optimise your network
- Ongoing monitoring, maintenance and support
- Cost, timeline and performance targets for Australian installs
- Pre-install checklist for your installer or DIY setup
- Key takeaways
- The case for treating Wi-Fi as infrastructure, not a utility
- Techbug’s business Wi-Fi services for Australian businesses
- Useful sources and further reading
Why business Wi-Fi differs from home Wi-Fi
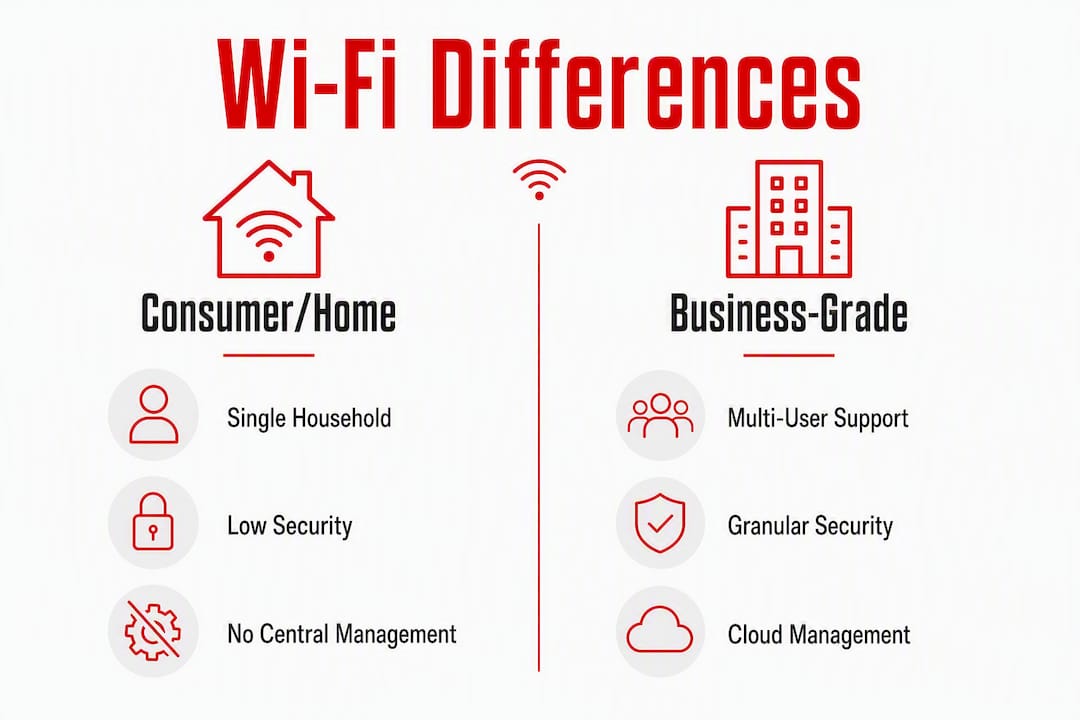
Consumer mesh systems are built for convenience. Business Wi-Fi is built for accountability, security, and scale. The gap between them is not just marketing; it shows up in real operational consequences.
Using a consumer router in a business environment means you have no centralised management console, no VLAN segmentation to isolate guest traffic from your accounting server, and no captive portal for customer access. Worse, consumer APs use “sticky client” behaviour: a device clings to a distant AP instead of roaming to a closer one, which kills VoIP call quality. When something breaks, there is no audit log, no remote diagnostics, and no SLA.
Cloud-managed enterprise systems give you the configuration visibility, captive portals, and granular security controls that consumer hardware simply cannot match. The table below shows where the practical differences land.
| Feature | Consumer / home gear | Business-grade managed APs |
|---|---|---|
| Best for | Single household, low density | Office, retail, multi-floor, high-density |
| Management model | Local web UI, per-device | Cloud or on-prem controller, centralised |
| Security features | WPA2-PSK only | WPA3, 802.1X, RADIUS, captive portal, VLAN |
| Scalability | Add another router; conflicts likely | Controller scales to hundreds of APs |
| Cabling / backhaul | Wireless mesh or single Ethernet port | Cat6/Cat6A wired backhaul to PoE switch |
The practical consequence of ignoring this table: a 20-person office running a consumer mesh system will spend more on troubleshooting dropped calls and security incidents over two years than a properly specced managed install would have cost upfront.
How to plan your business wifi setup: audit users, apps and space
Planning is where most SMB installs go wrong. Owners buy hardware based on the box’s coverage claim, skip the site survey, and end up with dead zones in the boardroom.
Site survey basics
A site survey comes in two forms. A predictive survey uses floor plan software to model RF propagation before installation; it is fast and cheap, and good enough for straightforward single-floor offices. An active survey uses a laptop with Wi-Fi analysis software walking the actual space after APs are placed; it produces a real heatmap and catches interference from concrete pillars, metal racking, or neighbouring networks. For any deployment with more than four APs, an active post-installation survey is worth the cost.
Before you buy anything, answer these questions:
- Peak concurrent users: how many devices connect simultaneously at the busiest point of the day?
- App mix: do staff use VoIP softphones, video conferencing (Teams, Zoom), or cloud-hosted POS? These are latency-sensitive and need priority QoS treatment.
- IoT inventory: printers, scanners, smart TVs, building sensors, and EFTPOS terminals all consume radio capacity and may need their own VLAN.
- PCI/POS requirements: if you process card payments over Wi-Fi, PCI DSS mandates network segmentation.
- Uptime requirements: does a Wi-Fi outage stop your business entirely? If yes, you need redundancy and a UPS in the comms cabinet.
AP sizing reference
Design by capacity, not coverage. The rule of thumb is one AP per typical moderate office zone size, but that breaks down fast in high-density environments. A conference room running five concurrent video sessions needs a dedicated AP regardless of its floor area.
| Office size | Typical device count | Starting AP estimate | Notes |
|---|---|---|---|
| Small | Up to 20 | 2–3 APs | Single floor, open plan |
| Medium | 20–30 | 4–8 APs | Mix of offices and open areas |
| Large | 60–100 | 8–12 APs | Multi-zone; dedicated APs for boardrooms |
| Multi-floor / high-density | More than 100 | More than 12 APs | Per-floor design; stairwells need coverage |
DIY vs professional install checkpoints:
- Fewer than 3 APs, single floor, no VLANs, no VoIP: DIY is viable
- 4+ APs, multiple VLANs, VoIP, POS, or PCI scope: hire a professional
- Any multi-floor deployment or heritage building with thick masonry: professional mandatory
How to select your ISP, gateway and business-grade hardware
Choosing an ISP plan
Your Wi-Fi is only as fast as the pipe feeding it. For most Australian SMBs, a business-grade NBN or fibre plan with a symmetric upload speed matters more than raw download figures. VoIP and video conferencing consume upload bandwidth, and contention ratios on business plans are lower than residential equivalents. Run a wired speed test at the gateway using a tool like Speedtest CLI or iPerf3 before assuming your Wi-Fi is the bottleneck.
Gateway and firewall
For offices with fewer than 25 staff, a business-grade router with integrated firewall (such as a Ubiquiti UniFi Dream Machine Pro or a Cisco Meraki MX appliance) handles routing, firewall, and VPN in one unit. Larger deployments benefit from a dedicated firewall appliance sitting upstream of the switching layer. The key requirement is that the gateway supports VLAN trunking to your managed switches.
Hardware checklist
- Wi-Fi standard: Wi-Fi 6 (802.11ax) is the current minimum for new installs; Wi-Fi 6E adds the 6 GHz band for high-density environments; Wi-Fi 7 is emerging but hardware costs remain high in 2026
- Access points: enterprise-grade APs from vendors like Ubiquiti UniFi or Cisco Meraki, both widely available through Australian distributors
- PoE switch: sized to your AP count with enough PoE budget (watts) to power every AP simultaneously, plus 20% headroom
- Cable category: Cat6 or Cat6A for all backhaul runs; Cat6A supports 10 Gbps and gives headroom for future Wi-Fi standards
- Controller model: cloud-managed (subscription, accessible anywhere) vs on-premises controller (one-off cost, local dependency)
Cloud-managed vs on-premises controller
Cloud-managed platforms like Cisco Meraki charge an annual licence per device but give you remote management, automatic firmware updates, and centralised alerting from any browser. Ubiquiti UniFi can run a cloud controller or a local UniFi Network Server (a small appliance or a VM), with no per-device licence fee. For most Australian SMBs, the Ubiquiti model offers strong value; Meraki suits organisations that want vendor-backed SLAs and deeper enterprise integrations.
Consumer mesh vs managed APs at a glance:
- Backhaul: consumer mesh uses wireless backhaul, halving throughput per hop; managed APs use wired Cat6 backhaul
- Management: consumer gear is per-device; managed APs use a single controller pane
- Security: consumer gear tops out at WPA2-PSK; managed APs support WPA3, 802.1X, RADIUS, and per-SSID VLAN assignment
- Scalability: adding a second consumer router creates conflicts; adding a managed AP takes minutes in the controller
Pro Tip: Check Wi-Fi 6 compatibility with your existing devices before committing. Older laptops and phones connect fine on Wi-Fi 6 APs, but they will not get the full throughput benefit. Read Techbug’s Wi-Fi 6 overview for a plain-language breakdown of what actually changes for end users.
Best practices for access-point placement and installation
Placement fundamentals
Place APs based on geometry and device density, not aesthetics. Ceiling-mounted APs in the centre of a zone outperform wall-mounted units in corners. Aim for 15–20% cell overlap between adjacent APs so devices can roam without dropping; too much overlap causes co-channel interference, too little creates dead zones. Avoid mounting APs directly above metal server racks, inside comms cabinets, or in hallways where they serve no users.
Wired backhaul is not optional above 15 staff
Wired backhaul is the standard for any professional deployment. In offices with more than roughly 15 employees, every AP should run a dedicated Cat6 or Cat6A cable back to a managed PoE switch. Wireless mesh backhaul cuts usable bandwidth by roughly half per hop. That is acceptable in a home; it is not acceptable when many people are on a video call. For a deeper look at why wired connections outperform wireless backhaul, the Ethernet vs Wi-Fi comparison on Techbug’s site covers the performance ceiling in plain terms.
PoE and cabling notes
Each AP draws between 12 W and 25 W depending on the model and whether it uses PoE or PoE+. Add up the total wattage for all APs and confirm your switch’s PoE budget covers it with headroom. Multi-gig uplinks (2.5 Gbps or 10 Gbps) between your core switch and gateway future-proof the switching layer for Wi-Fi 6E and Wi-Fi 7 throughput.
Common installation mistakes
The three mistakes that cause the most callbacks: mounting APs in corners where they serve walls instead of people; daisy-chaining unmanaged switches under desks to extend cabling (this creates broadcast storms and kills performance); and under-speccing the PoE switch budget so APs power-cycle randomly under load.
Pro Tip: Label every cable run at both ends before the ceiling tiles go back in. A simple label printer and a cable register spreadsheet save hours of troubleshooting later. While you are in the comms cabinet, install a UPS. It is one of the cheapest investments you can make to protect hardware and reduce downtime from power fluctuations, which are more common in older Australian commercial buildings than most people expect.
Network security configuration to apply during setup
Security checklist
- Change all default management credentials immediately; enable MFA on the controller and gateway
- Create a dedicated management VLAN accessible only from a trusted admin device
- Set a firmware update policy: automatic for APs and switches, scheduled for gateways
- Back up your controller configuration after every change; store backups off-site or in cloud storage
- Disable unused SSIDs, ports, and management protocols (Telnet, HTTP)
VLAN-to-SSID mapping
Segmenting traffic by VLAN is the single most effective security control in a business Wi-Fi deployment. A practical mapping for most Australian SMBs:
- SSID: CorpStaff → VLAN 10: authenticated staff devices; WPA3-Enterprise or 802.1X; full internal network access
- SSID: CorpVoice → VLAN 20: VoIP handsets and softphones; QoS priority; isolated from guest and IoT
- SSID: GuestAccess → VLAN 30: customer and visitor Wi-Fi; captive portal; internet-only; client isolation enabled
- SSID: IoT → VLAN 40: printers, smart TVs, sensors, EFTPOS; no access to staff VLAN; outbound internet only
- SSID: POS → VLAN 50: PCI-scoped devices only; strictly segmented; monitored for compliance
WPA3-Enterprise and 802.1X
WPA3-Enterprise with 802.1X authentication and a RADIUS server is the right choice for any business handling sensitive data, operating under PCI DSS, or with more than ten staff. Instead of a shared password, each user or device authenticates with individual credentials or a certificate. When an employee leaves, you revoke their account in Active Directory or your identity provider; the Wi-Fi access disappears automatically. Identity-based access reduces credential sprawl and makes revocation workflows far simpler than rotating a shared PSK across 30 devices.
For smaller offices not yet ready for a full RADIUS deployment, WPA3-Personal with a strong, regularly rotated passphrase is a reasonable interim step, provided guest and IoT traffic are still VLAN-segmented.
Guest Wi-Fi and captive portals
Guest VLANs with client isolation and a captive portal are the baseline for any customer-facing Wi-Fi. Captive portal types include click-through (lowest friction), email capture, voucher codes, social login, and paid access. If you collect email addresses through a captive portal, you have data retention obligations under the Australian Privacy Act 1988; keep a clear privacy notice on the portal page and do not retain data longer than necessary.
Pro Tip: Move away from shared pre-shared keys for staff networks. Certificate-based device onboarding or SSO integration means you never need to email a Wi-Fi password to a new starter, and you never need to change it when someone leaves. Pair this with cybersecurity training for staff so employees understand why they should not share credentials or connect personal devices to the corporate SSID.
Zero-trust basics for Wi-Fi:
- Never trust a device based on SSID alone; authenticate the user or device identity
- Apply least-privilege firewall rules between VLANs; staff VLAN should not reach IoT VLAN by default
- Log all authentication events and review alerts weekly
- Segment remote-access VPN traffic the same way you segment on-site VLANs
How to test, validate and optimise your network
Tools for the job
- WiFiman (Ubiquiti, free): Wi-Fi analyser app for Android and iOS; shows RSSI, channel utilisation, and neighbouring networks
- iPerf3: command-line throughput tester; run between two wired hosts first, then repeat wirelessly to isolate Wi-Fi from WAN bottlenecks
- Ekahau Site Survey or NetSpot: predictive and active survey software for heatmap generation; Ekahau is the professional standard, NetSpot is a lower-cost option for smaller deployments
- Spectrum analyser: a hardware tool or USB adapter that shows non-Wi-Fi interference (microwave ovens, Bluetooth, DECT phones); worth renting for high-density or problematic environments
Performance targets
RSSI target: −67 dBm minimum at every client location for reliable VoIP and video. Signal strength above −67 dBm gives adequate SNR for voice; below −70 dBm, packet loss and jitter climb. For data-only areas where VoIP is not used, −70 dBm is an acceptable floor.
Acceptable SNR for voice is 25 dB or higher. Jitter below 30 ms and packet loss below 1% are the thresholds for acceptable VoIP quality; most enterprise QoS configurations target jitter under 10 ms.
Verification steps
- Run iPerf3 wired-to-wired first to confirm the LAN and WAN are not the bottleneck
- Repeat iPerf3 wirelessly from the centre of each zone; compare to the wired baseline
- Walk the floor with WiFiman open; confirm RSSI stays above −67 dBm throughout
- Test roaming by walking between AP coverage zones on a VoIP call; a properly configured 802.11r fast roaming setup reduces handoff time from roughly 500 ms to roughly 50 ms, which is the difference between a brief stutter and a dropped call
- Validate the captive portal on the guest SSID from a personal device
- Generate a final heatmap and compare it to the predictive survey; document any gaps
Interpreting results and fixing issues
If RSSI is low in a zone, try increasing AP transmit power before adding another AP; sometimes a power adjustment is all that is needed. Persistent dead zones usually mean an AP needs repositioning or an additional AP is required. High channel utilisation on 2.4 GHz is common in Australian commercial buildings with many neighbouring networks; move devices to 5 GHz or 6 GHz bands and enable band steering. If throughput is low despite good RSSI, check for a cabling fault or a daisy-chained unmanaged switch in the backhaul path.
Ongoing monitoring, maintenance and support
A business Wi-Fi network is not a set-and-forget installation. The maintenance tasks that matter most are firmware patching, health monitoring, and periodic re-surveys as the office changes.
Maintenance schedule:
- Weekly: review controller alerts for AP offline events, high error rates, and authentication failures
- Monthly: check AP CPU and memory utilisation; review DHCP lease counts against pool sizes; confirm captive portal is functioning
- Quarterly: run a brief active survey or WiFiman walk to check for new interference sources or coverage gaps caused by office rearrangements
- Annually: full performance review; assess whether AP count and hardware generation still match current device density and application mix; review firmware versions and end-of-support dates
Monitoring essentials:
- Alert on any AP going offline for more than five minutes
- Monitor controller CPU and memory; a cloud-managed platform handles this automatically
- Track captive portal authentication failures, which can indicate a configuration drift or a certificate expiry
- Set DHCP pool exhaustion alerts; a full pool silently prevents new devices from connecting
What to ask a vendor or installer
Before signing a support contract, get clear answers on: SLA response times (four-hour on-site vs next-business-day), whether remote monitoring is included or billed separately, annual licence costs for cloud-managed platforms, on-site support windows, and whether full handover documentation (network diagram, VLAN map, AP placement plan, controller credentials) is included at project close.
Managed service vs ad-hoc support
A managed Wi-Fi subscription makes financial sense when your business depends on connectivity for revenue (retail, hospitality, professional services), when you lack internal IT staff, or when the cost of an unplanned outage exceeds the monthly subscription fee. Ad-hoc support works for very small offices with simple single-SSID setups and low downtime tolerance. The break-even point for most Australian SMBs is around 10–15 staff; above that, the time cost of managing firmware, monitoring, and troubleshooting internally usually exceeds a managed service fee. Techbug’s managed IT services include proactive monitoring and on-site support for Brisbane and across Australia.
Cost, timeline and performance targets for Australian installs
Cost ranges
The figures below are estimates based on comparable professional installation data and should be confirmed with local quotes, as Australian labour and hardware costs differ from overseas benchmarks.
Cost reference: UK-sourced professional installation data puts small single-floor offices (approximately 2 APs) at £750–£2,000, and complex multi-floor or high-density deployments at £4,000–£15,000+. Typical Australian installs follow a broadly similar structure, though hardware costs in AUD are generally higher due to import margins, and labour rates reflect local market conditions. For a small single-floor office (around 2 APs), expect professional installation to fall within £750–£2,000; for complex multi-floor or high-density deployments, costs range from £4,000 to £15,000+.
Project timeline
- Week 1: site survey, floor plan review, hardware specification and ordering
- Week 2: cabling works (if required) and comms cabinet preparation
- Week 3: AP installation, configuration, testing, heatmap validation, and handover documentation
Most SMB installs complete in 2–3 weeks end-to-end. Complex multi-floor deployments with significant cabling works can run to four to six weeks.
Performance targets summary
- RSSI: −67 dBm minimum at every client device for voice and data reliability
- AP density: start at one AP per 1,000–1,500 sq ft; increase density for conference rooms running multiple concurrent video sessions
- Jitter: under 30 ms for acceptable VoIP; target under 10 ms for enterprise-grade voice
- Packet loss: below 1% for voice; below 0.1% for video conferencing
Pre-install checklist for your installer or DIY setup
Hand this list to your installer at the first meeting, or work through it yourself before ordering hardware.
Site and user information:
- Floor plans (PDF or CAD) with dimensions and room labels
- Peak concurrent user count and device types (laptops, phones, tablets, IoT)
- List of latency-sensitive apps (VoIP platform, video conferencing tool, POS system)
- Preferred SSID names and any existing naming conventions
- VLAN requirements and whether PCI scope applies
- Power and comms-room access windows (after hours, weekends?)
Technical checks:
- Confirm Cat6 or Cat6A cabling availability; note any runs that need replacing or extending
- Calculate PoE budget: total AP wattage plus 20% headroom
- Confirm UPS is installed or planned for the comms cabinet
- Run a wired speed test at the gateway and record the result
- Note any multi-gig uplink requirements if deploying Wi-Fi 6E or Wi-Fi 7 APs
Quote and project fields:
- Preferred project start date and completion deadline
- Installed AP count (from the sizing table above)
- On-site access windows for cabling and installation crews
- Budget band (helps the installer recommend appropriate hardware tiers)
- Whether ongoing managed monitoring is required post-installation
Key takeaways
A properly planned business wifi setup with wired backhaul, VLAN segmentation, and WPA3 or 802.1X authentication delivers reliable, secure connectivity that scales as your business grows.
| Point | Details |
|---|---|
| Start with a site survey | Map your space, user density, and app mix before buying any hardware. |
| Wired backhaul is mandatory above 15 staff | Every AP needs a Cat6/Cat6A run to a managed PoE switch; wireless mesh backhaul halves usable bandwidth per hop. |
| Target RSSI −67 dBm | This is the minimum signal strength for reliable VoIP and video at every client location. |
| VLAN segmentation protects the business | Separate staff, guest, IoT, POS, and voice traffic onto dedicated VLANs to contain breaches and meet PCI requirements. |
| Techbug for local managed support | Techbug provides site surveys, cabling audits, RADIUS/802.1X setup, and ongoing managed Wi-Fi monitoring for Australian businesses. |
The case for treating Wi-Fi as infrastructure, not a utility
Most small business owners think about Wi-Fi the same way they think about electricity: it should just work, and the cheapest option that keeps the lights on is fine. That framing is understandable, but it is the reason so many Australian offices are running on consumer mesh gear that drops VoIP calls, has no guest isolation, and cannot tell you which device is hammering the bandwidth at 2 PM on a Tuesday.
The businesses that get this right treat the wireless network the same way they treat their server or their phone system: something worth specifying properly, installing correctly, and maintaining on a schedule. The payoff is not just fewer dropped calls. It is the ability to onboard a new staff member and give them network access in minutes, revoke it the same day they leave, and know that your guest Wi-Fi cannot reach your accounting software because the VLANs physically prevent it.
The other thing worth saying plainly: the site survey step gets skipped more often than any other. Owners assume they know where the dead zones are, or they trust the AP vendor’s coverage radius claim. Neither is reliable. A 30-minute walk with WiFiman before installation costs nothing and prevents the most common remediation call, which is “we need another AP in the boardroom.”
For businesses in older Brisbane or Sydney commercial buildings, thick concrete and steel-reinforced floors create RF environments that no predictive model fully captures. An active post-installation survey is not optional in those environments; it is the only way to confirm the design actually worked.
Techbug’s business Wi-Fi services for Australian businesses
Techbug works with Australian businesses to design, install, and manage Wi-Fi networks that are built to last. The services cover everything discussed in this guide: site surveys and heatmap validation, cabling audits, managed AP deployment using vendor-agnostic hardware, RADIUS and 802.1X configuration, VLAN segmentation, captive portal setup, and ongoing proactive monitoring. For businesses that want the security side handled end-to-end, Techbug’s IT security services include network hardening, WPA3-Enterprise configuration, and compliance-aligned segmentation for PCI and privacy requirements.
The next step is straightforward: contact Techbug for a site survey or a scoped quote. Techbug’s team is based in Brisbane and supports businesses across Australia, with a vendor-agnostic approach that means you get the hardware that fits your environment, not whatever a single distributor is pushing this quarter. Reach out via Techbug’s managed IT services page to start the conversation.
Useful sources and further reading
The sources below were used for figures, technical targets, and best-practice guidance throughout this guide.
- ACMA — Australian Communications and Media Authority: Australia’s spectrum regulator; confirms equipment compliance requirements for Wi-Fi installations.
- Purple — How to set up Wi-Fi for your business: Source for the −67 dBm RSSI target and enterprise-grade voice/data performance benchmarks.
- Purple — Office Wi-Fi setup guide: Covers cloud-managed architecture rationale and the case for centralised controllers over consumer gear.
- iFeelTech — What we tell clients about Wi-Fi before we start: Practical source for AP density rules, wired backhaul requirements, Cat6/Cat6A cabling guidance, 802.11r fast roaming data, and UPS recommendations.
- Connection Technologies — Business Wi-Fi installation costs 2026: UK-market cost benchmarks (£750–£2,000 for small offices; £4,000–£15,000+ for complex deployments) used as a comparative reference for Australian budgeting.
- SpeedtestHQ — Wi-Fi for small business: guest, employee and POS segmentation: Covers guest VLAN configuration, client isolation, and captive portal options.
- EPB — Business Wi-Fi installation guidance: Supports the professional installation vs DIY decision framework and the cost of skipping a site survey.
- Techbug — Managed IT services: Techbug’s managed IT and Wi-Fi monitoring services for Australian businesses seeking ongoing support.
- Techbug — IT security services: Covers WPA3-Enterprise, RADIUS, and network segmentation engagements for compliance-focused deployments.