
The Essential Eight are eight prioritised mitigation strategies developed by the Australian Signals Directorate (ASD) and the Australian Cyber Security Centre (ACSC) to make it significantly harder for adversaries to compromise internet-connected networks. If your organisation operates under the Public Governance, Performance and Accountability Act (PGPA) or the Protective Security Policy Framework (PSPF), these controls are not optional. For suppliers, contractors, and Queensland businesses working with government clients, they are increasingly a procurement baseline.
Your immediate next step: identify which assets are in scope, collect your current evidence (patch logs, MFA enrolment data, admin account lists, backup restore records), and determine your starting maturity level. If you do not have that evidence ready, commission a scoping engagement before anything else.
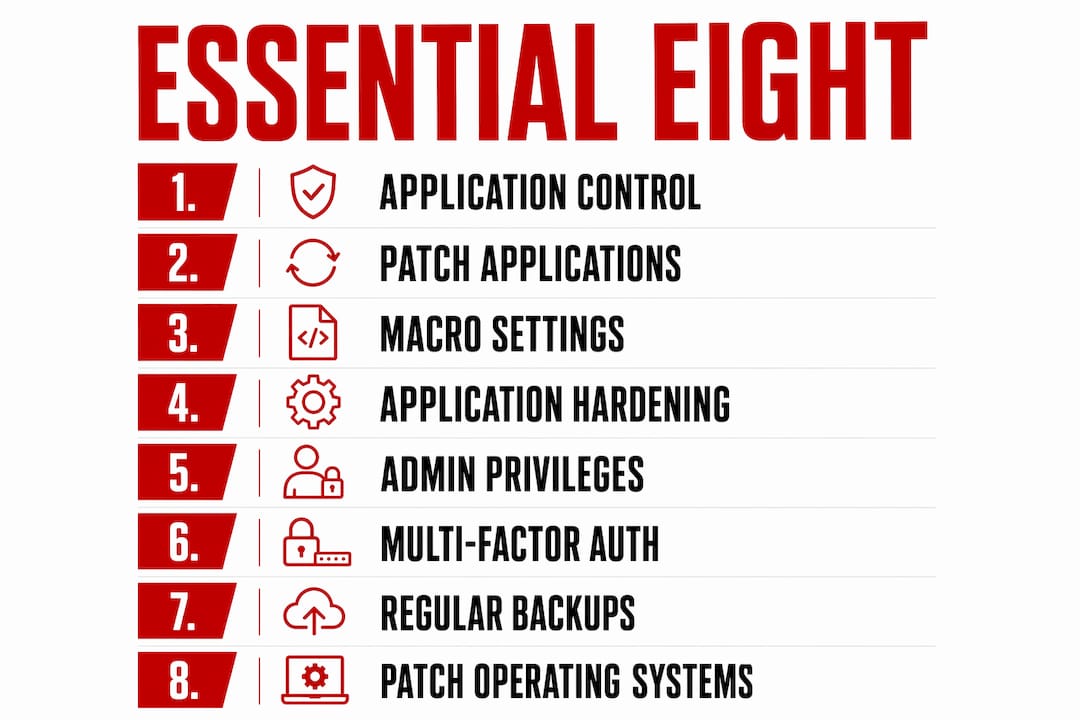
The eight controls at a glance:
- Application control — only approved applications can execute on endpoints
- Patch applications — third-party and browser software patched on a defined cycle
- Configure Microsoft Office macro settings — macros blocked or restricted to trusted, signed sources
- User application hardening — browsers and PDF readers stripped of risky features
- Restrict administrative privileges — admin rights limited to accounts that genuinely need them
- Multi-factor authentication (MFA) — additional verification required for all privileged and internet-facing access
- Regular backups — tested, immutable, ransomware-resilient copies of critical data
- Patch operating systems — OS vulnerabilities patched within defined windows based on maturity level
The maturity model runs from Level 0 (controls not implemented) through to Level 3 (fully implemented, enforced, monitored, and automated). Commonwealth non-corporate entities are generally expected to achieve a moderate maturity level across all eight controls. The ASD is clear that the framework was designed primarily for Microsoft Windows environments; cloud-native, Linux, and operational technology (OT) stacks need supplementary mapping to the Information Security Manual (ISM).
Treat the Essential Eight as a risk-reduction foundation, not a complete security programme. Pairing it with a Zero Trust architecture and broader ISM controls is what separates genuine resilience from a compliance checkbox.
Table of Contents
- What each of the eight controls actually does
- How the maturity model works and what assessors look for
- How an Essential Eight assessment works in practice
- How to prioritise and sequence implementation without disrupting operations
- Who must comply and how it affects procurement and insurance
- Realistic timelines, costs, and resourcing models
- How Techbug helps Australian organisations reach Essential Eight maturity
- Key takeaways
- The compliance trap is real, and most organisations fall into it
- Techbug’s Essential Eight services for Queensland businesses
- Official sources and further reading
What each of the eight controls actually does
The eight mitigations address three distinct threat objectives: preventing malware delivery, limiting the blast radius of a successful attack, and recovering from incidents. Understanding the security intent behind each control helps you prioritise effort and explain trade-offs to non-technical stakeholders.
1. Application control
Security intent: prevent unauthorised or malicious code from executing, even if it is delivered to an endpoint.
Application control uses allowlisting to permit only approved executables, libraries, scripts, and installers. On Windows environments, Microsoft AppLocker and Windows Defender Application Control (WDAC) are the standard mechanisms. At higher maturity levels, control extends beyond executables to DLLs and scripts. Assessors will typically request a current application allowlist, evidence of testing against the baseline, and logs showing blocked execution attempts. For a practical walkthrough of implementing application control in an Australian business context, the approach matters as much as the tooling.
Cloud and non-Windows note: container-based environments use image signing and admission controllers (e.g. Kubernetes OPA/Gatekeeper) as functional equivalents. OT environments often require vendor-specific whitelisting tools.
2. Patch applications
Security intent: close known vulnerabilities in third-party software before adversaries exploit them.
This control covers browsers (Chrome, Edge, Firefox), PDF readers, productivity suites, and other internet-facing applications. Patch cadence tightens at higher maturity levels: at the highest maturity level, critical patches to internet-facing applications are applied promptly after release. Assessors expect automated scanning evidence (biweekly at minimum), patch timelines, and a record of exceptions with compensating controls. Unpatched applications sitting on endpoints with no exception process are one of the most common reasons an assessment drops to Level 1.
3. Configure Microsoft Office macro settings
Security intent: prevent macro-based malware delivered via phishing documents from executing.
The control requires blocking macros from the internet by default and, at higher maturity levels, restricting execution to digitally signed macros from trusted publishers. Group Policy or Microsoft Intune are the standard enforcement mechanisms. Assessors look for a documented macro policy, evidence of Group Policy Object (GPO) deployment, and user communication records. Organisations that rely on legacy macro-enabled workflows need a migration plan before implementing this control at Level 2 or above.
4. User application hardening
Security intent: reduce the attack surface of commonly exploited browser and document features.
This covers disabling Flash (now universally deprecated), blocking web advertisements, disabling unneeded browser plugins, and configuring PDF readers to prevent execution of embedded content. At Level 2 and above, PowerShell is constrained to Constrained Language Mode. Assessors will check browser configuration baselines and endpoint management policy exports. The control is straightforward on managed Windows fleets but requires additional tooling for BYOD or unmanaged endpoints.
5. Restrict administrative privileges
Security intent: limit the accounts that can make system-wide changes, reducing the damage an attacker can do after initial compromise.
Admin accounts should be separate from standard user accounts, used only for administrative tasks, and subject to just-in-time (JIT) or privileged access workstation (PAW) controls at higher maturity levels. Assessors request a current admin account register, evidence of periodic review (at least annually at Level 2, more frequently at Level 3), and logs showing privileged activity. Stale admin accounts — former staff, service accounts with excessive rights — are a consistent finding in assessments.
6. Multi-factor authentication
Security intent: prevent credential theft from being sufficient to compromise accounts.
MFA is required for all users accessing internet-facing services and for privileged accounts at every maturity level. At the highest maturity level, phishing-resistant MFA such as hardware tokens or FIDO2 passkeys is recommended for privileged access instead of less secure methods. Assessors check MFA enrolment logs, conditional access policies, and whether legacy authentication protocols (basic auth, NTLM) have been disabled. Microsoft Entra ID (formerly Azure AD) conditional access is the most common implementation path for Microsoft 365 environments.
7. Regular backups
Security intent: preserve the ability to recover critical data and systems after a ransomware attack or destructive incident.
Backups must be more than copies. ASD guidance stresses tested, immutable, and ransomware-resilient recovery processes. At the intermediate maturity level, backups are stored offline or in an immutable state and tested regularly. At the highest maturity level, restoration is tested against defined recovery objectives. Assessors ask for backup logs, restore test records, and evidence that backup accounts are separate from production admin accounts. Cloud backup solutions that provide immutable storage and air-gapped copies satisfy the technical requirement; the test record is what most organisations miss.
8. Patch operating systems
Security intent: eliminate OS-level vulnerabilities that enable privilege escalation and lateral movement.
OS patching windows are generally wider than application patching windows at lower maturity levels, but tighten significantly at Level 3. Unsupported operating systems (end-of-life Windows versions, unpatched Linux distributions) must be removed from scope or isolated with compensating controls. Assessors expect automated patch deployment evidence, a current asset register showing OS versions, and a documented exception process for systems that cannot be patched on the standard cycle.
How the maturity model works and what assessors look for
The maturity model is the measurement backbone of the framework. A maturity rating is determined by the weakest control or weakest evidence trail across the environment. An organisation cannot claim a moderate maturity overall if one control is not sufficiently implemented or lacks evidence.
| Maturity level | Security outcome | Assessor expectation | Typical evidence examples |
|---|---|---|---|
| Level 0 | Controls not implemented or ineffective | No evidence of implementation | Missing logs, no policy, inconsistent patching |
| Level 1 | Controls partially implemented; some attacks may succeed | Basic documentation and some technical evidence | Patch reports with gaps, partial MFA rollout, informal admin review |
| Level 2 | Controls largely implemented; many attacks mitigated | Consistent evidence across all controls, documented exceptions | Patch reports, MFA enrolment logs, macro policy documentation, backup tests |
| Level 3 | Controls fully implemented and monitored with automation | Automated evidence, policy enforcement, continuous telemetry | Logs and reports showing timely patching and robust MFA, backups tested regularly |
Moving from Level 2 to Level 3 almost always requires automation and policy-driven processes. The ASD’s own guidance is explicit: manual processes cannot sustain Level 3 at scale. Lack of automation is the single biggest resource barrier organisations face when targeting the top tier.
Evidence assessors commonly request:
- Current asset register (endpoints, servers, cloud workloads in scope)
- Patch scan reports with timestamps and remediation timelines
- MFA enrolment and conditional access policy exports
- Admin account register with last-reviewed date
- Backup logs and restore test records (including date, scope, and outcome)
- Application allowlist and blocked-execution logs
- Macro policy GPO or Intune configuration export
- Browser and application hardening configuration baselines
Common assessment gaps that lower a whole-environment rating:
- Asset register out of date, meaning patch coverage cannot be verified for the full scope
- Backup restore tests documented informally (email threads rather than signed records)
- MFA deployed for most users but legacy authentication protocols still enabled, leaving a bypass
- Admin accounts reviewed annually on paper but stale accounts present in Active Directory
- Patch reports covering managed endpoints only, with unmanaged or BYOD devices excluded from scope
Telemetry and vulnerability dashboards, such as those described in Tenable’s Cyber Exposure materials, can assist with continuous verification and patch prioritisation, giving assessors the automated evidence trail that manual processes cannot reliably produce.
How an Essential Eight assessment works in practice
Assessments follow a consistent structure whether you run them internally, engage a third-party assessor, or use a hybrid model. The process has four phases.
Step-by-step assessment process
- Scoping — define the boundary: which systems, users, and data are in scope. Crown-jewel assets and high-risk user groups (privileged users, remote workers, finance teams) should be in scope from the start. Document the scoping rationale; assessors will review it.
- Evidence collection — gather the artefacts listed above. Automated collection (configuration exports, scan reports, log extracts) is far more defensible than screenshots or verbal confirmation.
- Technical verification — credentialed vulnerability scans, configuration baseline comparisons, MFA bypass testing, backup restore tests. This is where gaps between documented policy and actual technical state surface.
- Report and remediation plan — the assessor produces a maturity rating per control, identifies gaps, and recommends a prioritised remediation roadmap. The report should map findings to specific evidence and maturity level criteria.
Assessment options: self-assessment, third-party, or hybrid
Self-assessment suits organisations with a capable internal security team and a clear audit trail. The risk is confirmation bias: teams tend to rate their own controls more generously than an external assessor would. Self-assessments are acceptable for internal baseline tracking but are rarely sufficient for formal attestation to government clients or insurers.
Third-party assessment by an accredited assessor provides independent verification and a defensible report for procurement or regulatory purposes. For Commonwealth entities, ASD provides guidance on assessor expectations and the Essential Eight Explained PDF sets the assessment criteria. Cost and lead time are the main constraints for smaller agencies.
Hybrid model — internal teams collect evidence and run technical checks; an external assessor reviews the evidence and validates findings. This is the most cost-effective approach for mid-sized organisations and Queensland government agencies that need a formal rating without the full cost of an end-to-end external engagement.
Tools and mechanisms assessors frequently expect to see:
- Endpoint detection and response (EDR) platform with centralised telemetry
- Configuration management tooling (Microsoft Intune, SCCM, or equivalent)
- Centralised logging and SIEM (Microsoft Sentinel, Splunk, or equivalent)
- Automated patch management with scan-to-deploy reporting
- Privileged access management (PAM) solution for admin account governance
- Backup platform with immutable storage and restore test scheduling
Pro Tip: Before engaging an external assessor, run a gap analysis against the ASD’s own maturity model criteria. Fix the obvious gaps first — stale admin accounts, missing backup restore records, legacy auth protocols — so the assessor’s time is spent on genuine ambiguities, not low-hanging remediation.
How to prioritise and sequence implementation without disrupting operations
The most common implementation mistake is attempting an organisation-wide rollout without prior scoping. Start with high-value assets and high-risk user cohorts, then phase controls and evidence collection outward.
Prioritisation roadmap
Phase 1 — Reduce malware delivery (quick wins, low friction):
MFA and macro restriction deliver the highest risk reduction for the least operational disruption. MFA rollout on Microsoft 365 via Entra ID conditional access can be completed in weeks for most organisations. Macro policy via Group Policy or Intune is a configuration change, not a deployment project. Start here.
Phase 2 — Limit blast radius (moderate engineering effort):
Restrict administrative privileges and user application hardening. Privilege restriction requires an admin account audit, which surfaces stale accounts and over-privileged service accounts. Budget time for stakeholder communication: business units that rely on local admin rights will push back. Pilot with IT staff first, then high-risk user groups.
Phase 3 — Harden the platform (heavier engineering work):
Application control and patch automation. Application control is the most operationally disruptive control to implement. A pilot on a defined workload type (e.g. call centre desktops) before broad rollout prevents business-stopping blocklist gaps. Patch automation requires a tested deployment pipeline with rollback capability.
Phase 4 — Verify and recover:
Backup resilience and OS patching. Backup integrity testing and OS patch automation close the recovery and persistence gaps. These controls are technically straightforward but require ongoing operational discipline.
Automation and sequencing notes
Policy-as-code approaches (using tools like Microsoft Intune configuration profiles, PowerShell DSC, or Ansible for Linux environments) reduce configuration drift and produce the automated evidence trail that Level 3 requires. Centralised telemetry from an EDR platform feeds both the technical verification step and the continuous monitoring posture that separates a point-in-time audit from genuine security.
For cloud and SaaS environments, the ASD notes the framework was designed for Windows-centric IT networks. Cloud-native workloads on AWS, Azure, or Google Cloud require mapping to equivalent controls: cloud security posture management (CSPM) tools, identity federation with phishing-resistant MFA, and immutable object storage for backups. For OT and industrial control systems, supplementary ISM controls are necessary; the Essential Eight alone does not address the specific risk profile of those environments. Organisations that navigate hybrid or cloud-heavy stacks will find iSET+ a useful reference for emerging security technology governance in those contexts.
Pro Tip: Stage rollouts using pilot groups and define rollback criteria before you start. A failed application control deployment that blocks a critical business application at 8 AM on a Monday will set the entire programme back by months. Pilot, document, expand.
Who must comply and how it affects procurement and insurance
The Essential Eight is mandatory for Australian non-corporate Commonwealth entities under the PSPF and the PGPA Act. These organisations are required to implement the controls and report their maturity level. The expectation for most Commonwealth entities is at least Level 2 across all eight controls, with higher-risk entities targeting Level 3.
For the private sector, the framework carries no direct legislative mandate. However, the practical compliance pressure is significant and growing:
- Government procurement: Commonwealth and state government buyers increasingly require suppliers to attest to an Essential Eight maturity level as part of tender evaluation. Queensland Government agencies are guided by the Queensland Government Enterprise Architecture (QGEA) Essential Eight guideline, which applies the framework to Queensland government ICT environments.
- Cyber insurance: Insurers are using Essential Eight maturity as an underwriting criterion. Organisations that cannot demonstrate at least Level 1 across all controls face higher premiums or coverage exclusions for ransomware and business interruption claims.
- Supply chain obligations: If your organisation handles Commonwealth data or operates as a managed service provider to government clients, contractual obligations may require you to meet a specified maturity level and provide evidence on request.
The relationship between the Essential Eight and the ISM is complementary, not duplicative. The ISM is a comprehensive controls catalogue covering hundreds of security requirements; the Essential Eight is a prioritised subset designed for baseline implementation. Microsoft’s compliance guidance maps Essential Eight controls to Microsoft 365 and Azure capabilities, which is useful for organisations already invested in the Microsoft stack.
Practical procurement callouts:
- Include Essential Eight maturity level attestation as a mandatory tender criterion for ICT suppliers handling sensitive data
- Require evidence packages (not just self-attestation) for contracts above a defined risk threshold
- Specify the maturity level required by contract, not just “compliance with the Essential Eight”
- Build a review cadence into supplier contracts (annual re-attestation at minimum)
- For urgent queries, the ACSC operates a 24/7 hotline: 1300 CYBER1 (1300 292 371)
For SMEs navigating these obligations, Techbug’s IT compliance guide for SMEs covers the practical steps for meeting government procurement requirements without an in-house security team.
Realistic timelines, costs, and resourcing models
Finance and delivery teams consistently underestimate the time and resource required to progress from Level 1 to Level 2, and from Level 2 to Level 3. The timeline and resourcing for essential cybersecurity projects vary widely with organisation size, tooling, and capabilities. Project durations can range from a few weeks to over a year depending on scope and maturity goals, with cost drivers including licensing, engineering time, and assessor fees.
Key cost drivers to budget for:
- EDR and endpoint management licensing (Intune, Defender for Endpoint, or equivalent)
- SIEM or centralised logging platform
- PAM tooling for admin account governance at Level 3
- Immutable backup storage (cloud object storage with object lock, or offline media)
- Assessor fees for third-party or hybrid assessments
- Internal staff time for evidence collection, stakeholder communications, and change management
Resourcing models by organisation type:
Small agencies and Queensland SMBs with fewer than 50 users typically lack the internal security capability to deliver and maintain the Essential Eight without external support. A managed IT security service that covers patch management, MFA administration, backup monitoring, and endpoint telemetry is usually more cost-effective than hiring a dedicated security analyst.
Mid-sized departments (50–500 users) can often deliver the initial implementation internally but benefit from a managed service for ongoing monitoring and evidence collection. The hybrid model — internal delivery, external verification — suits this cohort well.
Large agencies and departments with dedicated security teams should focus internal effort on automation, policy-as-code, and continuous telemetry, using external assessors for periodic formal verification.
Success metrics to track during delivery:
- Time-to-patch: mean time from patch release to deployment, tracked by control category
- MFA coverage: percentage of users and privileged accounts with MFA enrolled
- Admin account reduction: number of active admin accounts versus baseline
- Backup restore time: actual restore duration versus defined RTO
- Backup integrity: percentage of restore tests completed successfully in the period
Pro Tip: Track time-to-patch as a weekly metric from day one, even before your patch automation pipeline is complete. The baseline data becomes your Level 1 evidence and shows assessors a trajectory of improvement, which matters when you are mid-implementation.
How Techbug helps Australian organisations reach Essential Eight maturity
Techbug’s delivery approach for the Essential Eight follows a phased model designed for Australian SMBs and government-adjacent organisations that need to move from baseline to a defensible maturity level without disrupting day-to-day operations.
Delivery phases:
- Discover: asset inventory, current-state evidence review, and gap analysis against the maturity model. This phase produces a scoping document and a prioritised remediation roadmap.
- Scope and pilot: implement quick-win controls (MFA, macro policy, application hardening) on a defined pilot group. Validate evidence collection processes before broad rollout.
- Expand: roll out remaining controls (application control, patch automation, privilege restriction, backup resilience) across the full environment in sequenced waves.
- Verify: conduct internal gap assessment against ASD criteria, prepare evidence packages, and support formal third-party assessment if required.
- Sustain: ongoing managed monitoring, patch management, backup verification, and periodic re-assessment to maintain maturity level as the environment changes.
Outcome metrics Techbug uses to demonstrate progress:
- Maturity level per control, tracked against the ASD criteria at each phase gate
- MFA enrolment percentage across all users and privileged accounts
- Patch cadence reports showing time-to-patch against maturity level targets
- Backup restore test records with dates, scope, and outcomes
- Admin account register with review dates and reduction trend
Techbug’s vendor-agnostic approach means the tooling recommendation follows the environment, not a preferred vendor relationship. For Microsoft 365-heavy environments, the delivery path uses native Entra ID, Intune, and Defender capabilities. For mixed or cloud-native environments, Techbug maps controls to equivalent mechanisms and supplements with ISM guidance where the Essential Eight does not directly apply.
For organisations ready to start, the first step is a scoping engagement: a structured conversation about your current environment, your maturity target, and the fastest path to defensible evidence. Techbug’s IT security services cover the full delivery path from initial gap analysis through to ongoing managed security.
Key takeaways
The Essential Eight is a mandatory baseline for Commonwealth entities and a de facto procurement standard for any Australian organisation working with government clients or seeking cyber insurance coverage.
| Point | Details |
|---|---|
| Mandatory for Commonwealth entities | Non-corporate Commonwealth entities must implement the Essential Eight under the PSPF/PGPA framework. |
| Weakest control sets the rating | A single control with incomplete evidence drops the whole-environment maturity rating, regardless of other controls. |
| Level 3 requires automation | Moving from Level 2 to Level 3 demands policy-driven, automated processes; manual evidence collection cannot sustain it. |
| Backups need tested restore records | Immutable storage alone is insufficient; assessors require documented restore tests with dates, scope, and outcomes. |
| Techbug delivers phased implementation | Techbug’s discover-scope-pilot-expand-verify model gives Australian SMBs and government-adjacent organisations a structured path to defensible Essential Eight maturity. |
The compliance trap is real, and most organisations fall into it
There is a version of Essential Eight implementation that looks good on paper and provides almost no actual security improvement. It involves ticking boxes, generating reports, and passing an assessment without meaningfully changing the organisation’s risk posture. The controls are met on the day of the audit; six months later, patch cycles have slipped, backup restore tests have not been run, and stale admin accounts have accumulated again.
The framework’s designers at ASD are aware of this. The shift from Level 2 to Level 3 is deliberately structured to require continuous, automated verification rather than point-in-time evidence. But even Level 3 organisations can fall into the compliance trap if they treat the maturity rating as a destination rather than a current state.
The more useful mental model is continuous risk management. Passing an assessment is a snapshot. What actually reduces your exposure is the operational discipline behind the controls: the patch cycle that runs every fortnight without someone manually triggering it, the backup restore test that happens on a schedule and produces a signed record, the admin account review that catches a stale account before an attacker does.
The Essential Eight also does not address everything. It was designed for internet-connected Windows environments, and it shows. Organisations with significant SaaS footprints, cloud-native workloads, or OT systems need to supplement it with ISM controls and, increasingly, a Zero Trust architecture that assumes breach rather than relying on perimeter controls. The broader IT security picture matters as much as the eight controls themselves.
My practical advice: treat the Essential Eight as the floor, not the ceiling. Use it to build the evidence discipline and operational habits that make your security posture genuinely measurable. Then build upward from there.
Techbug’s Essential Eight services for Queensland businesses
Getting to a defensible Essential Eight maturity level is not a one-off project. It requires ongoing patch management, MFA administration, backup verification, and periodic re-assessment as your environment changes. For most Queensland SMBs and government-adjacent organisations, that is more than an internal IT team can sustain alongside day-to-day support.
Techbug’s managed IT services cover the controls that matter most: managed patching for applications and operating systems, MFA implementation and ongoing administration, ransomware-safe backup monitoring with tested restore records, endpoint management and application control, and formal gap assessments against the ASD maturity criteria. The vendor-agnostic approach means Techbug recommends the tooling that fits your environment, not a preferred product stack.
For organisations ready to start, the entry point is a scoping engagement: a structured review of your current environment, your maturity target, and a prioritised roadmap. For those already mid-implementation who need a formal assessment, Techbug supports evidence preparation and third-party assessment coordination. Speak with the Techbug team about a cybersecurity assessment tailored to your organisation’s scope and maturity target.
Official sources and further reading
The documents below are the primary references for Essential Eight implementation and assessment in Australia. Download them before engaging an assessor.
-
Essential Eight | Cyber.gov.au — the ASD’s primary landing page for the framework. Contains the current controls list, maturity model overview, and links to all official guidance documents. Start here.
-
Essential Eight Explained (ASD PDF, November 2023) — the definitive reference document. Contains the maturity model criteria per control, evidence requirements, and assessment guidance. The maturity model tables in this document are what assessors use to evaluate evidence.
-
Essential Eight Explained (web version) | Cyber.gov.au — the web-accessible version of the explained document, updated periodically. Useful for quick reference and linking in internal policy documents.
-
QGEA Essential Eight guideline | Queensland Government — Queensland Government’s specific guidance applying the Essential Eight to Queensland government ICT environments. Mandatory reading for Queensland agencies and their ICT suppliers.
-
ACSC Essential Eight overview | Microsoft Learn — Microsoft’s mapping of Essential Eight controls to Microsoft 365 and Azure capabilities. Contains licensing notes and configuration guidance for Entra ID, Intune, Defender, and related services.
-
Tenable Cyber Exposure Study: Essential Eight — maps Essential Eight strategies to verification approaches and dashboarding for continuous assessment. Useful for security teams building a continuous compliance monitoring capability.
-
ThreatLocker: Essential Eight explained — practical explainer covering patch cadence expectations by maturity level and implementation notes for application control and user hardening.
-
ACSC 24/7 hotline: 1300 CYBER1 (1300 292 371) — for urgent cyber security incidents and queries. The ACSC also provides assessment course references and formal assessor guidance through the cyber.gov.au portal.
-
Information Security Manual (ISM) — available at cyber.gov.au. The comprehensive controls catalogue that supplements the Essential Eight for specialised environments (cloud, OT, Linux). Cross-reference the ISM when the Essential Eight does not directly address a control requirement in your environment.