
IT compliance is defined as the practice of aligning your organisation’s IT systems, policies, and processes with legal, regulatory, and industry requirements that protect data and secure systems. For Queensland business leaders, the stakes are real. GDPR cumulative fines have reached €7.1 billion globally, and that figure reflects what regulators will pursue when organisations fall short. IT compliance is not a one-off project. It is a continuous operational discipline that touches access control, data protection, incident response, and audit readiness every single day.
What are the main IT compliance standards SMEs should know?
Every business that handles customer data, processes payments, or stores health information operates under at least one compliance framework. Knowing which ones apply to your business is the first step toward meeting your IT regulatory requirements.
The most common frameworks are:
- GDPR (General Data Protection Regulation): Applies to any business handling personal data of EU residents. Covers data collection, storage, processing, and breach notification.
- Privacy Act 1988 (Australia): The Australian Privacy Principles govern how organisations collect, use, and disclose personal information. Relevant to most Queensland SMEs.
- PCI DSS (Payment Card Industry Data Security Standard): Mandatory for any business that accepts, processes, or stores card payments. Covers network security, access control, and monitoring.
- HIPAA (Health Insurance Portability and Accountability Act): Applies to health data. Relevant for Queensland healthcare providers with US-based clients or partners.
- ISO 27001: An internationally recognised information security management standard. Voluntary but widely required by enterprise clients and government contracts.
- SOC 2 (Service Organisation Control 2): A US-originated audit standard covering security, availability, and confidentiality. Increasingly required by enterprise buyers of SaaS and managed services.
- NIST CSF (National Institute of Standards and Technology Cybersecurity Framework): A voluntary US framework widely adopted as a best-practice baseline for risk management.
Some frameworks are mandatory by law. Others are voluntary but effectively required to win contracts with larger clients or government agencies. ISO 27001 certification, for example, signals to enterprise buyers that your security controls are independently verified. That signal translates directly into sales.
Pro Tip: If you are unsure which frameworks apply to your business, start with the Australian Privacy Act and PCI DSS if you process card payments. Add ISO 27001 if you sell to enterprise or government clients.
What are the core IT compliance requirements SMEs must implement?
Meeting IT compliance standards requires specific technical and procedural controls. These are not optional extras. They are the baseline that auditors check first.
Identity and access management
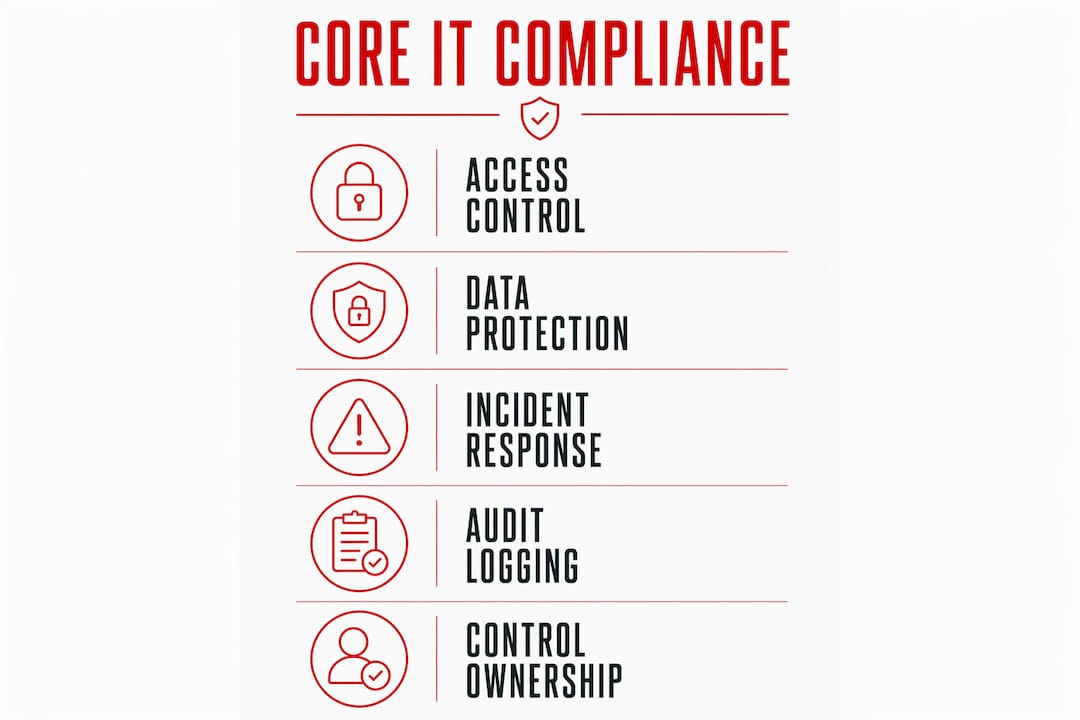
Access control is the most common source of audit findings. MFA, RBAC, and quarterly access reviews must be in place and demonstrably enforced. Role-based access control (RBAC) means staff only access the systems and data their role requires. Multi-factor authentication (MFA) adds a second verification layer beyond passwords. Quarterly access reviews confirm that permissions remain appropriate as roles change.
Employee access must be deprovisioned within 24 hours of termination. That deadline exists because former employees with active credentials represent an immediate data exposure risk. Automated deprovisioning workflows remove human error from this process entirely.
Data protection and classification
Data classification defines which information is sensitive, confidential, or public, and applies handling rules accordingly. Encryption protects data at rest and in transit. Retention and deletion policies specify how long data is kept and when it must be securely destroyed. Without these policies documented and enforced, auditors will flag gaps regardless of what tools you have installed.
Incident response and breach notification
Every business needs a written incident response plan. GDPR requires breach notifications to relevant authorities within 72 hours of detection. The Australian Privacy Act has similar mandatory notification requirements under the Notifiable Data Breaches scheme. A plan that exists only as a document is not enough. Staff must know their roles, and the plan must be tested at least annually.
Audit logging and evidence management
Audit logs record who accessed what, when, and what they did. Logs, timestamps, and linked enforcement records are required by auditors. Screenshots and verbal confirmation do not satisfy modern audit standards. Every control must produce verifiable, timestamped evidence that it was enforced consistently over time.
Pro Tip: Assign a named owner to every compliance control. That person is responsible for enforcement, exception handling, and producing evidence when auditors ask. Without named ownership, controls drift.
How can SMEs prepare for and maintain ongoing IT compliance audits?
Audit preparation is not something you do in the weeks before an assessment. Compliance is a continuous lifecycle requiring named control owners and ongoing verifiable evidence. Businesses that treat audits as annual events consistently struggle to produce the evidence auditors need.
A seven-step audit roadmap gives SMEs a repeatable structure:
- Select your framework. Identify which standards apply to your business based on industry, geography, and client requirements.
- Define scope. Determine which systems, data types, and business processes fall within the compliance boundary.
- Conduct a gap assessment. Compare your current controls against framework requirements and document every gap.
- Remediate gaps. Prioritise gaps by risk level and assign owners with deadlines for each remediation task.
- Run an internal audit. Test your controls before an external assessor does. Identify weaknesses while you still have time to fix them.
- Engage a third-party assessor. External audits provide independent verification and are required for certifications like ISO 27001 and SOC 2.
- Maintain documentation. Keep policies, evidence, and control records current. Auditors review documentation history, not just current state.
Common audit pitfalls to avoid
Many organisations fail compliance not because they lack tools, but because they cannot demonstrate that their tools are operational and enforced. The three most common pitfalls are missing evidence, inconsistent enforcement, and unclear ownership. A firewall that is installed but not monitored provides no audit value. A policy that exists but is not followed creates liability rather than protection.
Internal audits should run at least annually. For businesses under PCI DSS or SOC 2, quarterly reviews of specific controls are standard practice. The frequency matters less than the consistency. Auditors look for a pattern of ongoing diligence, not a single point-in-time snapshot.
What role does automation play in IT compliance for SMEs?
Modern IT environments are complex. Automation tools address the complexity of managing 100-plus SaaS applications, improving compliance efficiency across the board. Manual processes cannot keep pace with the volume of access events, configuration changes, and policy checks that compliance requires.
Automation contributes to compliance in several concrete ways:
- Continuous monitoring: Automated tools check security controls around the clock and alert on violations in real time, rather than waiting for a quarterly review to surface a problem.
- Evidence collection: Compliance platforms pull logs, access records, and configuration data automatically, building the audit-ready evidence trail that auditors require.
- Identity governance: Automated provisioning and deprovisioning workflows enforce the 24-hour access removal deadline without relying on manual IT tickets.
- Shadow IT discovery: Automated tools identify unauthorised applications employees have connected to company data, closing a common compliance gap that manual reviews miss entirely.
- Policy violation alerts: When a user’s access exceeds their role permissions or a configuration drifts from the approved baseline, automated alerts flag the issue immediately.
Automation reduces manual effort by continuously monitoring security controls, collecting audit evidence, and alerting on violations. That reduction in manual effort is not just about efficiency. It means your team spends time fixing problems rather than hunting for evidence that a problem exists.
For Queensland SMEs with lean IT teams, managed IT support services fill the gap between what automation can do and what requires human judgement. Techbug’s proactive monitoring and managed IT services give businesses the coverage of a full security team without the overhead of building one in-house.
Key takeaways
IT compliance requires continuous enforcement, named control ownership, and verifiable audit evidence across every framework your business operates under.
| Point | Details |
|---|---|
| Know your frameworks | Identify which standards apply based on your industry, data types, and client requirements. |
| Enforce access controls | Implement MFA, RBAC, and 24-hour deprovisioning to meet identity management requirements. |
| Document everything | Auditors require timestamped logs and linked evidence, not screenshots or verbal confirmation. |
| Follow a seven-step audit roadmap | Structure your audit preparation to avoid resource-heavy, last-minute scrambles. |
| Use automation | Continuous monitoring and automated evidence collection reduce manual effort and close compliance gaps faster. |
Why IT compliance is harder than it looks, and what actually works
Compliance programmes fail for a predictable reason. Business leaders treat them as a project with a finish line. They bring in a consultant, tick the boxes, get the certificate, and move on. Six months later, staff have changed, systems have been added, and the controls that passed the audit are no longer enforced. The certificate is real. The compliance is not.
What I have seen work consistently is treating compliance like payroll. Nobody asks whether payroll is “done.” It runs every fortnight because the consequences of skipping it are immediate and obvious. Compliance needs the same treatment. Controls run. Evidence collects. Owners review. Exceptions get escalated. That cycle never stops.
The hardest part for SMEs is ownership. When nobody is formally responsible for a control, it drifts. I have seen businesses with excellent tools and zero compliance posture because every team assumed another team was managing the evidence. Assigning a named owner to every control, even in a small team, changes that dynamic completely.
Automation is not a shortcut. It is the only realistic way for a business with a small IT team to maintain compliance across multiple frameworks simultaneously. The businesses I have seen handle audits well are the ones that automated evidence collection early, before they needed it. The ones that scramble are the ones that assumed a manual process would scale.
Queensland SMEs face the same regulatory expectations as large enterprises, with a fraction of the resources. The answer is not to hire a compliance team. It is to build a system that runs without one.
— Ru
How Techbug supports SME compliance in Queensland
Techbug works with Queensland businesses to build and maintain the IT controls that compliance frameworks require. With over 30 years of combined experience across cybersecurity, managed IT services, and cloud solutions, Techbug provides proactive monitoring, ransomware-safe backups, and staff security training. These are not add-ons. They are the operational backbone that keeps your compliance posture intact between audits. If your business needs expert support to meet its IT compliance obligations, Techbug’s team is ready to assess your current position and build a plan that fits your size and budget.
FAQ
What is IT compliance?
IT compliance is the practice of aligning your organisation’s IT systems, policies, and processes with legal, regulatory, and industry requirements. It covers data protection, access control, incident response, and audit readiness.
Which IT compliance standards apply to Queensland SMEs?
Most Queensland SMEs must comply with the Australian Privacy Act 1988. Businesses processing card payments also fall under PCI DSS. Those selling to enterprise or government clients often need ISO 27001 or SOC 2 as well.
How often should SMEs conduct IT compliance audits?
Internal audits should run at least annually. Businesses under PCI DSS or SOC 2 typically review specific controls quarterly. The goal is a consistent pattern of diligence, not a single annual snapshot.
What do auditors actually look for during an IT compliance audit?
Auditors require timestamped logs, linked enforcement records, and named control owners. Screenshots and verbal confirmation do not satisfy modern audit standards. Evidence must show that controls were enforced consistently over time.
How does automation help with IT compliance?
Automation continuously monitors security controls, collects audit evidence, and alerts on policy violations. It enforces access deprovisioning deadlines and discovers unauthorised applications, reducing the manual workload on small IT teams significantly.