
Managed IT security services are outsourced cybersecurity operations that provide 24/7 threat detection, incident response, and compliance support for small to medium businesses and startups. The industry term for the core delivery model is Managed Security Services, or MSS, though many providers now operate as Managed Detection and Response (MDR) providers with a full Security Operations Centre (SOC) behind them. For Queensland SMBs and startups, these services fill a gap that internal IT teams simply cannot close on their own. 42% of cyberattacks target small businesses, which makes outsourced, expert-led protection not a luxury but a practical necessity.
What do managed IT security services actually cover?
Managed IT security services go well beyond installing antivirus software. They are ongoing operational partnerships where human analysts actively hunt threats, triage alerts, and coordinate responses around the clock. That distinction matters because most breaches are not stopped by software alone. They are stopped by people who know what to look for and act fast when they find it.
The core functions typically included are:
- Continuous threat monitoring. A dedicated SOC watches your environment 24 hours a day, 7 days a week, 365 days a year. This covers nights, weekends, and public holidays when your internal team is offline.
- Incident detection and rapid response. Analysts investigate alerts in real time and contain threats before they spread. Managed SOCs reduce attacker dwell time significantly, which directly limits the damage a breach causes.
- Threat intelligence and proactive hunting. Providers feed current threat data into your environment and actively search for indicators of compromise before an alarm triggers.
- Compliance documentation and reporting. Automated logs, audit trails, and reports are generated continuously, so your business is always ready for a compliance review.
- Endpoint, network, and cloud security integration. Services connect with tools like SIEM (Security Information and Event Management), EDR (Endpoint Detection and Response), and XDR (Extended Detection and Response) platforms to give analysts a complete picture of your environment.
Managed cybersecurity services provide specialised skills across endpoint, network, identity, threat hunting, and incident response disciplines. These are disciplines that most SMBs cannot recruit for internally, let alone staff around the clock.
How do managed IT security services support compliance?
Regulatory compliance is one of the strongest business cases for outsourcing IT security management. Most SMBs operating in Queensland face obligations under frameworks including the Australian Privacy Act, the Australian Cyber Security Centre’s Essential 8, and, depending on their sector, international standards like NIST, SOC 2, HIPAA, and PCI DSS.
Meeting these frameworks requires more than good intentions. It requires documented controls, audit trails, and evidence of continuous monitoring. Providers now commonly include automated documentation and compliance reporting as part of their standard service delivery. That means your business generates the evidence it needs without your team spending hours compiling it manually.
The compliance benefits of managed cybersecurity include:
- Audit-ready reporting. Logs and reports are produced automatically and stored in formats that satisfy auditor requirements.
- Framework alignment. Providers map their controls to the specific frameworks your business must meet, whether that is the Essential 8, NIST CSF, or SOC 2 Type II.
- Reduced internal workload. Your team stops chasing compliance paperwork and focuses on running the business.
- Cyber insurance readiness. Insurers increasingly require evidence of continuous monitoring and documented incident response plans. A managed service provider delivers both.
- Risk governance support. Successful providers align security outcomes with client business objectives, which means compliance becomes part of how the business operates, not a separate burden.
Pro Tip: Before signing with any provider, ask them to map their service controls directly to the Australian Cyber Security Centre’s Essential 8. If they cannot do this clearly, they are not the right fit for an Australian SMB.
What should SMBs look for in a provider?
Choosing between managed IT security services providers is one of the most consequential decisions a small business makes. The wrong provider leaves gaps. The right one becomes an extension of your team.
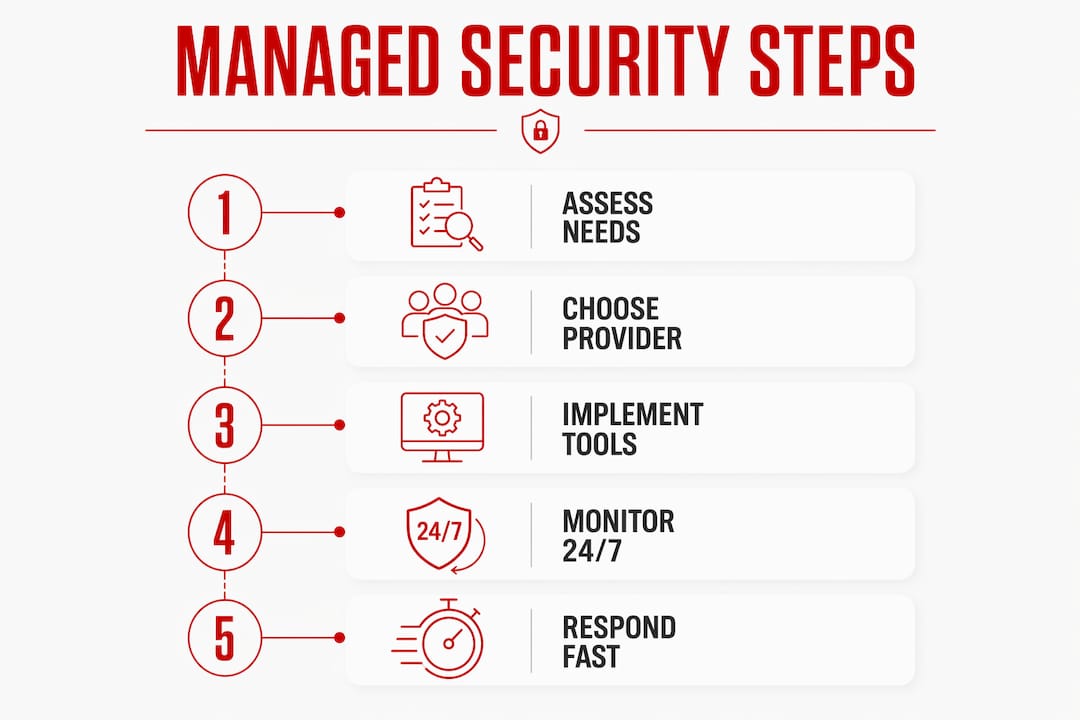
Human expertise, not just automation
The best providers deliver what the industry calls human-led, AI-enabled services. AI filters noise and speeds up triage. Human analysts make the judgement calls that determine whether an alert is a real threat or a false positive. Businesses that choose providers relying solely on automated tools often find their alerts go uninvestigated for hours.
Service level agreements that matter
Look for SLAs that specify Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR). These two metrics tell you exactly how fast your provider will find a threat and act on it. A provider that cannot commit to specific MTTD and MTTR figures is not confident in their own capability.
Certifications and compliance experience
Ask for evidence of relevant certifications. Providers working with Australian businesses should demonstrate familiarity with the Essential 8 and the Privacy Act. If your business operates in healthcare or finance, confirm the provider has direct experience with HIPAA or PCI DSS respectively.
Pricing and cost structure
- Per-user or per-device subscription. Pricing typically ranges from $10 to $30 per user or device monthly, depending on service complexity. This model suits growing businesses because costs scale with headcount.
- Tiered service levels. Entry-level plans cover monitoring and alerting. Advanced MDR tiers include active threat hunting, forensic investigation, and dedicated account management.
- All-inclusive versus modular. Some providers bundle everything into one fee. Others let you add services as your needs grow. Modular pricing suits startups watching cash flow closely.
- Contract terms. Month-to-month arrangements give flexibility. Annual contracts usually come with lower per-unit costs. Negotiate an exit clause tied to SLA performance.
Pro Tip: Request a sample monthly report from any provider before you sign. The quality of that report tells you exactly how much visibility you will have into your own security posture.
How do managed security services integrate with your existing IT setup?
Integration is where many SMBs hit unexpected friction. A managed security service does not replace your existing IT infrastructure. It connects to it, monitors it, and responds to threats within it.
Working alongside your internal team
Managed services complement internal IT teams rather than replace them. Your internal staff handle day-to-day IT support, hardware, and user requests. The managed security provider handles threat detection, response, and compliance reporting. Clear escalation workflows define who does what when an incident occurs.
The importance of internal cyber hygiene
The quality of what a managed provider can do depends heavily on the quality of data they receive. Patch management, password policies, and staff training remain the responsibility of the business itself. A provider monitoring an environment full of unpatched systems and weak passwords is fighting with one hand tied behind their back. Internal cyber hygiene is not optional. It is the foundation the managed service sits on.
Technology integration in practice
| Technology | Role in managed security | Who manages it |
|---|---|---|
| SIEM platform | Aggregates logs from all systems for analyst review | Managed provider |
| EDR agent | Monitors endpoint behaviour and isolates threats | Managed provider with client install |
| XDR platform | Correlates data across endpoints, network, and cloud | Managed provider |
| Patch management | Keeps systems current and reduces attack surface | Internal IT team |
| Staff awareness training | Reduces human error as an attack vector | Internal team or provider add-on |
Scalability is a genuine advantage of the managed model. As your Queensland business adds staff, opens new locations, or moves workloads to the cloud, your managed security coverage scales with it. You do not need to hire additional analysts. You adjust your subscription.
Key takeaways
Managed IT security services deliver enterprise-grade protection for SMBs by combining 24/7 human-led monitoring, automated compliance reporting, and technology integration that internal teams cannot replicate alone.
| Point | Details |
|---|---|
| 24/7 monitoring is non-negotiable | Threats do not stop at 5PM. Managed SOCs cover nights, weekends, and public holidays. |
| Compliance is built in | Automated documentation and audit-ready reports reduce the internal compliance workload significantly. |
| Pricing scales with your business | Subscription models from $10 to $30 per user monthly make managed security accessible for startups. |
| Internal hygiene still matters | Patch management, strong passwords, and staff training are your responsibility and affect service quality. |
| Choose providers with clear SLAs | MTTD and MTTR commitments are the clearest signal of a provider’s real capability. |
Why I think most SMBs underestimate the human element
The conversation around managed cybersecurity has shifted heavily toward AI and automation in the past two years. Every provider now leads with machine learning, automated playbooks, and AI-powered detection. That is not wrong. Those tools are genuinely useful. But they create a false sense of security when businesses assume the technology does the work on its own.
The talent shortage driving SMBs toward managed services is real. Hiring a qualified security analyst in Brisbane costs well above the average IT salary, and you need more than one to cover a 24/7 roster. That is the honest reason most small businesses cannot build this capability internally. Managed services solve that problem. But only if the provider actually has experienced analysts behind the platform.
The shift to outcomes-based security management is the most important trend I see for Queensland SMBs in 2026. The question is no longer “do we have security tools?” It is “can we demonstrate measurable risk reduction to our board, our insurer, and our regulator?” That requires human judgement, not just dashboards.
My honest advice: do not buy a managed security service based on the technology stack. Buy it based on the people who answer the phone at 2AM when something goes wrong.
— Ru
Techbug’s IT security services for Queensland businesses
Queensland SMBs and startups have a local option worth knowing about. Techbug, based in Brisbane, brings over 30 years of combined experience to IT security services for businesses across the state. The team takes a vendor-agnostic approach, which means you get the right solution for your environment rather than a product tied to a single vendor’s ecosystem.
Techbug delivers proactive monitoring, ransomware-safe backups, staff training, and an emergency response team ready when incidents occur. For businesses working toward Essential 8 compliance, Techbug’s cybersecurity services map directly to the ACSC framework. Whether you are a startup building your first security posture or an established SMB tightening your defences, Techbug offers a practical, cost-effective path forward. Contact the team to discuss what your business actually needs.
FAQ
What are managed IT security services?
Managed IT security services are outsourced cybersecurity operations that provide continuous threat monitoring, incident response, and compliance support. Providers operate a Security Operations Centre (SOC) staffed by human analysts who work around the clock on your behalf.
How much do managed IT security services cost?
Pricing typically follows a subscription model, ranging from $10 to $30 per user or device monthly, depending on service complexity and the level of MDR capability included.
Do managed security services replace my internal IT team?
No. Managed security services complement your internal IT team by handling threat detection, response, and compliance reporting. Your internal staff continue managing day-to-day IT support, hardware, and user requests.
What compliance frameworks do managed security providers support?
Most providers support frameworks including NIST, SOC 2, HIPAA, PCI DSS, and CMMC. Australian providers should also demonstrate alignment with the ACSC Essential 8 and the Privacy Act.
What is the difference between MSS and MDR?
Managed Security Services (MSS) typically covers monitoring and alerting. Managed Detection and Response (MDR) adds active threat hunting, forensic investigation, and faster, more hands-on incident response from dedicated analysts.