
For most complex Microsoft 365 tenant migrations, the right approach is an orchestrated, phased migration using Microsoft Migration Orchestrator for bulk workloads, supplemented by a commercial tool such as BitTitan MigrationWiz where native gaps exist — particularly for Teams chat history, granular SharePoint permissions, and Power Platform artefacts. That combination gives you the best balance of data fidelity, rollback safety, and timeline control.
Bring in a managed provider when any of these three conditions apply:
- Teams or Power Platform are in scope and your organisation cannot afford to lose chat history or accept manual Power Automate remediation.
- Hard M&A deadlines compress the project to under 12 weeks, leaving no room for internal trial-and-error.
- Limited internal migration experience means your team has not run a cross-tenant mailbox migration before and lacks a tested runbook.
Your immediate next step: run a discovery workshop to inventory workloads, map source identities, and size the pilot batch. The prerequisites checklist in Section 5 tells you exactly what to prepare before that workshop.
Table of Contents
- What business scenario are you actually migrating from?
- How do you choose the right migration model?
- What do you need to plan before any data moves?
- How do you prepare both tenants before migration starts?
- Which migration tools should you use for an Australian organisation?
- Cross-tenant mailbox migration: a step-by-step runbook
- How do you handle identity mapping and permissions correctly?
- How do you run a pilot, validate, and plan your rollback?
- What do you do after the migration completes?
- Your day-of runbook and migration weekend checklist
- Expert tips and common pitfalls to avoid
- Key takeaways
- The reality of tenant migrations in Australia
- Techbug’s managed migration service for Australian organisations
- Authoritative sources to use during planning
What business scenario are you actually migrating from?
The scenario shapes everything: timeline pressure, identity complexity, and which workloads carry the most risk. Getting this wrong at the start is how projects blow out.
| Scenario | Typical timeline | Identity complexity | Teams/Power Platform risk |
|---|---|---|---|
| Merger or acquisition | 8–16 weeks | High — two separate directories | High — chat history, guest access |
| Divestiture or spin-off | 12–20 weeks | High — partial directory split | Medium — selective data separation |
| Consolidation (multiple tenants) | — | Medium to high | Medium — depends on tenant count |
| Internal reorganisation / rebrand | 6–12 weeks | Low to medium | Low to medium |
| Partner-to-customer move | 4–10 weeks | Medium | Low |
Mergers and acquisitions carry the most pressure. The acquiring entity usually sets a go-live date before the migration team has even finished discovery, which means your runbook needs to be ready to compress. Divestitures are the opposite problem: the data separation requirement is strict, and moving the wrong mailboxes or SharePoint sites to the wrong tenant creates a compliance incident, not just a support ticket.
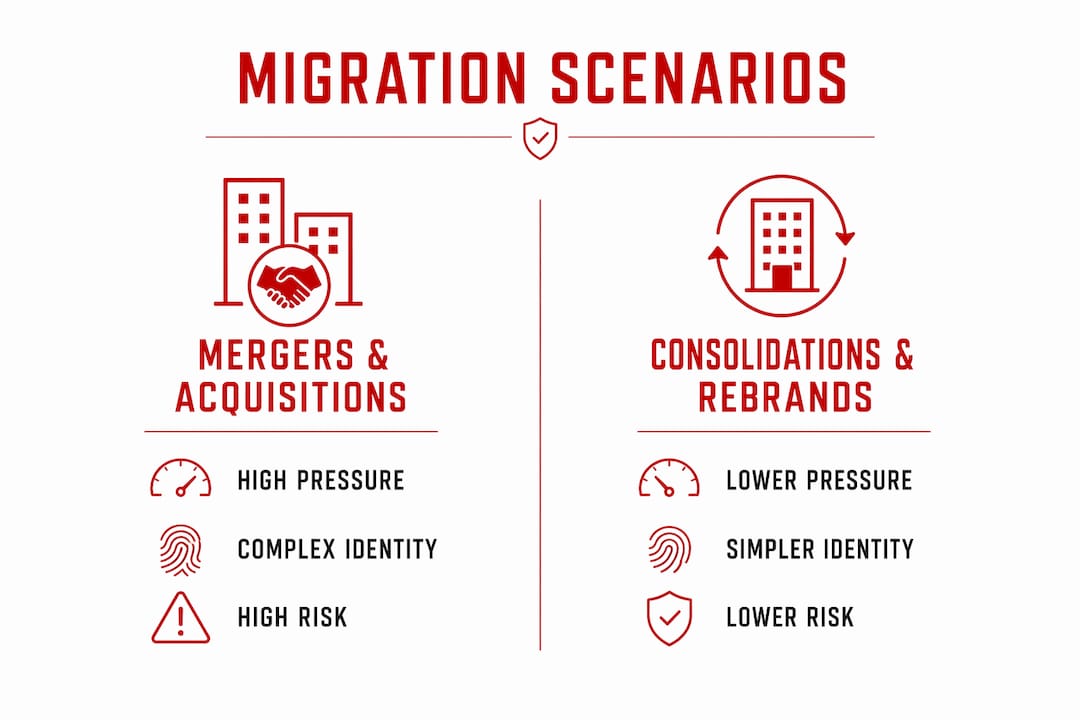
Consolidations and rebrands are generally lower risk but longer in elapsed time, because you are coordinating across more stakeholders without the urgency of a legal deadline. Partner-to-customer moves are the most contained, usually involving a small user set and a single domain transfer.
Scenarios involving M&A deadlines, complex identity splits, or Power Platform dependencies are the ones most commonly handled by a managed provider. If your project fits more than one of those descriptors, that is a strong signal to engage external support early.
How do you choose the right migration model?
Before picking an approach, answer these questions honestly: How many users are moving? How many domains are involved? Are Teams chat history and Power Platform in scope? What is the hard go-live date, and what happens if you miss it?
Big-bang migration
- Pros: Single cutover window, simpler DNS management, no extended coexistence period.
- Cons: All-or-nothing risk, long maintenance window, high user impact if something goes wrong.
- Primary risk vector: A failure mid-cutover with no staged fallback.
Best suited to small organisations (under 100 users) with simple workloads and a weekend maintenance window.
Phased or orchestrated migration
- Pros: Batches limit blast radius, allows validation between waves, supports rollback per batch.
- Cons: Extended coexistence period creates mail routing and free/busy complexity.
- Primary risk vector: Coexistence misconfiguration causing mail delivery failures between waves.
This is the default recommendation for most mid-to-large Australian organisations. Coexistence adds operational complexity that must be explicitly managed, but the risk is controllable with a well-designed mail routing plan.
Hybrid approach
A hybrid model runs orchestrated staging for the bulk of users, then executes a small big-bang cutover for domain transfer at the end. This is worth considering when you have a hard deadline but still want per-batch validation.
Pro Tip: In a hybrid model, complete all mailbox and OneDrive moves before the domain cutover window. The domain removal and re-addition creates a 30–60 minute disruption to email flow regardless of approach. Staging everything else beforehand means that window is your only production risk.
What do you need to plan before any data moves?
Tenant-to-tenant migration is commonly the most complex Microsoft 365 project because it moves identities, permissions, and collaboration history, not just files. Planning must cover identity strategy, workload sequencing, coexistence mechanics, licencing, and timeline estimation before a single batch runs.
Identity strategy
Cross-Tenant Identity Mapping (CTIM) is required for orchestrated migrations. It synchronises key attributes including ExchangeGUID and ArchiveGUID between source and target before any data movement begins. Azure AD Connect or Entra ID Connect handles on-premises hybrid scenarios, while cloud-only tenants rely on CTIM and pre-provisioned MailUser objects. Decide early whether users keep their existing UPN or receive a new one — this affects Outlook profile reconfiguration and end-user communication.
Workload sequencing
Microsoft recommends migrating Exchange mailboxes before or alongside Teams because Teams content depends on mailbox infrastructure. OneDrive and SharePoint share a permissions model, so migrating them together reduces remediation work. Power Platform environments should be assessed separately and moved last, after all identity dependencies are confirmed.
Coexistence mechanics
During a phased migration, mail routing between tenants, calendar free/busy sharing, and Teams federation must all be explicitly configured. Running two active tenants simultaneously creates user experience issues that are invisible until someone misses a meeting invite or a shared calendar stops working.
Licencing and CSP considerations
Budget for dual licencing during the transition period. Users in both tenants simultaneously need active licences in both. If your organisation procures through a Cloud Solution Provider (CSP), confirm with your partner that licence transfers and reassignments are handled correctly, particularly for Microsoft 365 Business Premium or E3/E5 plans. Australian CSP partners can assist with licence portability questions specific to local procurement agreements.
Timeline estimation
| Organisation size | Workload mix | Estimated duration |
|---|---|---|
| Under 100 users | Mail and OneDrive only | A few weeks |
| 100 users | Mail, OneDrive, SharePoint | Several weeks |
| several hundred users (M&A) | Full workload including Teams | Several weeks |
| — | Full workload including Power Platform | Several months |
A M&A integration with several hundred users typically takes weeks from discovery to go-live. Effort scales with workload complexity, not headcount alone — a 150-user organisation with Power Platform dependencies can take longer than a 400-user mail-and-OneDrive project.
How do you prepare both tenants before migration starts?
Get these steps done before any data moves. Skipping them is the single most common cause of mid-migration failures.
- Confirm admin roles. Assign Global Administrator or Exchange Administrator roles in both source and target tenants. Migration Orchestrator requires specific permissions in both directories.
- Register the migration application. Create an Azure AD app registration in both tenants with the required Microsoft Graph and Exchange Online API permissions. Note the Application (client) ID and generate a client secret.
- Configure the Organisation Relationship. In Exchange Online on both tenants, set up the OrganizationRelationship with
MailboxMoveEnabledand the correctMailboxMoveCapabilityvalues (Inbound on target, Outbound on source). - Set up CTIM. CTIM requires that ExchangeGUID and ArchiveGUID are matched and written to MailUser objects in the target tenant before migration batches start.
- Pre-provision target MailUser objects. For each source mailbox, create a corresponding MailUser in the target tenant with the correct ExternalEmailAddress pointing to the source tenant’s routing domain.
- Check conditional access policies. Confirm that conditional access rules in the target tenant will not block newly migrated users from authenticating on day one.
- Export source attributes. Run a PowerShell export of ExchangeGUID, ArchiveGUID, LegacyExchangeDN, and ProxyAddresses for all source mailboxes. Example pattern:
Get-Mailbox -ResultSize Unlimited | Select-Object DisplayName, ExchangeGuid, ArchiveGuid, LegacyExchangeDN, EmailAddresses | Export-Csv .source-mailbox-attributes.csv -NoTypeInformation
- Import attributes to target MailUsers. Use the exported CSV to stamp the matching attributes on each target MailUser object, then verify with
Get-MailUserbefore proceeding. - Secure service account credentials. Store all client secrets and service account passwords in Azure Key Vault or an equivalent secrets manager. Never embed credentials in migration scripts.
- Validate the migration endpoint. Run
Test-MigrationServerAvailabilityagainst the cross-tenant migration endpoint from the target tenant to confirm connectivity before creating any batches.
Migration Orchestrator moves content — mailboxes, OneDrive, chats, meetings — but does not move identities. Administrators must provision users and complete identity mapping independently before the orchestrator can do its job.
Which migration tools should you use for an Australian organisation?
Microsoft provides a native Migration Orchestrator for coordinated multi-workload migrations alongside workload-specific cross-tenant tools. Third-party solutions remain common for complex scenarios, and most real-world projects use both.
When native tools are the right call
- Migration Orchestrator handles mailboxes, OneDrive, Teams meetings, and Teams chats in coordinated batches. It is the right starting point for any project where those workloads are the primary scope.
- Cross-tenant mailbox migration via Exchange MRS is the underlying engine for mailbox moves and is well-suited to mail-only or mail-plus-OneDrive projects.
- Native tools are lower cost (included with eligible licences), have direct Microsoft support, and are the simplest path for straightforward workloads.
When to add a third-party tool
Native tools do not fully preserve Teams chat history, granular SharePoint permissions, or some Power Platform artefacts in every scenario. BitTitan MigrationWiz, available through Australian CSP and reseller partners, closes these gaps with dedicated connectors for SharePoint permissions, Teams channel content, and archive mailboxes.
- Use MigrationWiz when SharePoint site permissions must be preserved at the item or folder level.
- Use it when Teams chat history is a contractual or compliance requirement.
- Use it when Power Platform environments need structured migration rather than manual rebuild.
Australia-specific considerations
Australian organisations should confirm that their chosen tool vendor has local partner support and can schedule runbook execution within AEST/AEDT business hours. CSP licence procurement for MigrationWiz typically flows through an Australian Microsoft partner. Check whether your existing managed IT services agreement covers migration tooling costs, or whether they need to be budgeted separately.
The two-tool pattern
Most projects pair native Microsoft tooling for bulk workloads with a commercial tool to close gaps. Re-evaluate native capabilities at scoping rather than assuming they cannot handle your scenario — the Migration Orchestrator has expanded its supported workloads significantly. Use native for the bulk of mailboxes and OneDrive, then deploy MigrationWiz specifically for the workloads where native falls short.
Cross-tenant mailbox migration: a step-by-step runbook
Mailbox migration is the backbone of any Office 365 tenant transfer. Get this right and the rest of the project has a solid foundation.
Pre-move checks
- Identify all mailboxes on litigation hold or with preservation policies. Mailboxes on hold may block migration — contact your compliance or legal team before attempting to move them.
- Check archive mailbox status for each user. Archives must be accounted for separately in batch planning.
- Document mailbox sizes. Large mailboxes (over 50 GB) need dedicated batch slots and longer sync windows.
- Audit delegated mailbox permissions and shared mailbox access. These are not automatically preserved post-cutover.
- Confirm all target MailUser objects exist with correct ExchangeGUID values stamped.
Batch creation and migration steps
- Build a CSV file with target tenant email addresses (the
.onmicrosoft.comaddress for each user). - Create the migration batch from the target tenant:
New-MigrationBatch -Name T2TBatch01 -SourceEndpoint <YourEndpointName> -CSVData ([System.IO.File]::ReadAllBytes('batch01-users.csv')) -Autostart -TargetDeliveryDomain <targettenant>.onmicrosoft.com
- Monitor batch progress with
Get-MigrationBatchandGet-MigrationUserto track per-mailbox status. - Run a delta sync pass 24–48 hours before cutover to minimise data lag.
- Complete the batch and trigger the final cutover sync.
- Update
targetAddresson source MailUser objects to point to the target tenant routing domain. - Remove migration endpoints and OrganizationRelationships after all batches complete.
Pro Tip: Run the cross-tenant mailbox migration validation script before creating any batches. It checks all source and target objects simultaneously and surfaces attribute mismatches in one pass, saving hours of per-mailbox troubleshooting.
Common pitfalls
- Holds blocking moves. A mailbox under litigation hold will fail silently unless you check hold status before batching.
- Delegated permissions not preserved. Shared mailbox access and delegate permissions must be manually re-granted in the target tenant after cutover.
- Teams meetings not updated. Meeting URLs are invalid in the target tenant after migration. Users must remove and recreate Teams meetings.
- Outbox items not migrated. Items in the Outlook Outbox are client-side and will not transfer.
How do you handle identity mapping and permissions correctly?
Silent data loss often occurs during reconciliation when source identities do not have clean matches in the destination. Systematic remapping and verification are not optional extras.
CTIM essentials
CTIM matches source and target user objects by synchronising ExchangeGUID, ArchiveGUID, LegacyExchangeDN, and immutable IDs. Without correct attribute mapping, the Migration Orchestrator cannot associate source content with the right target mailbox.
| Source attribute | Target object | Verification check |
|---|---|---|
| ExchangeGUID | MailUser.ExchangeGuid | `Get-MailUser |
| ArchiveGUID | MailUser.ArchiveGuid | Populated if archive exists in source |
| LegacyExchangeDN | MailUser.ExternalEmailAddress | ExternalEmailAddress present |
| ImmutableId | Azure AD user object | Matches source on-premises objectGUID (hybrid) |
| PrimarySmtpAddress | MailUser.ExternalEmailAddress | Points to source routing domain |
SharePoint and Teams permission remapping
SharePoint permissions are tied to source Azure AD object IDs. After cutover, any permission entry referencing a source identity becomes an orphaned access control entry. The remediation approach:
- Export all SharePoint site permissions before migration using PnP PowerShell or the SharePoint Admin Centre.
- Map source user object IDs to target user object IDs using the identity mapping table.
- After cutover, run a permission remediation script that replaces source object references with target equivalents.
- Verify by spot-checking five to ten sites per wave, confirming that target users can access content they previously had rights to.
External sharing links and guest user access are not preserved automatically after cutover. Build a guest-access remediation plan and re-invite workflow into the runbook before go-live.
Pro Tip: Document your identity mapping table as a living spreadsheet updated after every batch. Source UPN, target UPN, source object ID, target object ID, and migration status in one place. When a SharePoint permission issue surfaces post-cutover, this table is the first thing you reach for.
How do you run a pilot, validate, and plan your rollback?
A pilot is not optional. It is the only way to confirm your runbook works before production users are affected.
Pilot plan
- Select 10–20 users representing different workload profiles: a standard mailbox user, a shared mailbox owner, a Teams channel owner, a user with a large archive, and a user with SharePoint site ownership.
- Define acceptance criteria before the pilot runs: mail flow confirmed within 30 minutes of cutover, calendar free/busy visible from target, OneDrive files accessible, Teams channel membership intact.
- Run the pilot in a maintenance window. Do not run it on a Friday afternoon before a long weekend.
- Document every failure, its root cause, and the remediation step taken.
Validation metrics
- Mail flow: send a test message from source to target and target to source within 15 minutes of cutover.
- Calendar free/busy: confirm availability is visible across tenants.
- File access: open five OneDrive files and three SharePoint documents from the target tenant.
- Teams joinability: confirm the pilot user can join an existing Teams channel and post a message.
- Authentication: confirm no conditional access blocks on first login from the target tenant.
Rollback conditions and steps
Trigger a rollback if any of these occur during the cutover window: mail delivery failures lasting more than 30 minutes, more than 10% of pilot users unable to authenticate, or SharePoint access failures across multiple sites.
Rollback steps: freeze the migration batch using Stop-MigrationBatch, revert DNS MX records to the source tenant, re-enable source mailboxes if they were disabled, and notify the help desk to redirect user calls. The domain cutover is the hardest step to reverse — once the primary domain is removed from the source tenant and added to the target, a 30–60 minute email disruption is unavoidable regardless. Script and rehearse this step in the pilot before touching production.
During the cutover window, assign a single incident commander with authority to call a rollback. Communication cadence: status update to executives every 30 minutes, help desk briefed with a script for the five most common user issues before the window opens.
What do you do after the migration completes?
Post-migration is where projects quietly fail. Validation and decommissioning need as much rigour as the migration itself.
| Task | Owner | Timing |
|---|---|---|
| Verify all users can authenticate and access mail | IT admin | Day 1 |
| Re-authorise OAuth apps and third-party integrations | IT admin | Day 1–3 |
| Re-invite external guests and restore sharing links | IT admin / business owners | Day 1–5 |
| Validate SharePoint site access and permissions | IT admin | Day 1–5 |
| Confirm Teams membership and channel access | IT admin | Day 1–3 |
| Remove source tenant licences for migrated users | IT admin / finance | Week 2–4 |
| Decommission source tenant domains | IT admin | Week 4–8 |
| Confirm eDiscovery and retention policies in target | Compliance team | Week 2–4 |
| Remove migration endpoints and OrganizationRelationships | IT admin | Week 2 |
| Final sign-off and source tenant shutdown | Project sponsor | Week 8–12 |
Do not decommission the source tenant until retention and eDiscovery holds are confirmed in the target. Regulatory hold requirements under Australian Privacy Act obligations and any applicable industry frameworks mean source data may need to remain accessible for a defined period after migration. Confirm this with your legal or compliance team before removing domains or shutting down the source tenant. For guidance on cloud backup solutions before decommissioning, ensure all data is verifiably present in the target before any source deletion.
Your day-of runbook and migration weekend checklist
A runbook without a day-of checklist is a plan that falls apart at 2 AM. Keep this tight and assign every action to a named person.
Roles for the cutover window
- Migration lead: executes batch commands, monitors progress, calls go/no-go decisions.
- Network/DNS owner: executes MX, Autodiscover, and SPF/DKIM record changes on instruction.
- Help desk lead: manages user communications and escalates authentication failures.
- Incident commander: single authority to call a rollback.
Day-of runbook bullets
- T-48 hours: run final delta sync pass, confirm all pre-move checks complete, brief help desk.
- T-24 hours: confirm DNS TTLs reduced to 300 seconds, validate rollback scripts are ready.
- T-0 (cutover start): disable source mailboxes for the current batch, trigger final sync, confirm batch completion.
- T+15 minutes: execute DNS MX cutover, update Autodiscover records.
- T+30 minutes: send test emails in both directions, confirm free/busy, check Teams access.
- T+60 minutes: confirm no open P1 incidents, send executive status update.
- T+2 hours: confirm help desk call volume is within normal range, document any open issues.
Communication templates
Executive status update (every 30 minutes): “Migration wave [X] is [on track / delayed by Y minutes]. [N] users successfully migrated. No critical issues / [issue description and ETA to resolve]. Next update at [time].”
Help desk script for Outlook profile issues: “Your email account has been moved to a new system. Please close Outlook, open it again, and follow the prompts to reconfigure your profile. If the issue persists after two attempts, escalate to the IT migration team.”
Expert tips and common pitfalls to avoid
The failure modes in tenant migrations are predictable. They happen on almost every project that skips systematic verification.
Teams history loss
Teams chat history does not migrate cross-tenant with native tools. The Teams chat folder content is available for source tenant administrators to search and export after migration, but it does not appear in the target tenant inbox automatically. If chat history is a compliance or business requirement, plan a dedicated MigrationWiz track for Teams content before the project starts, not after users complain.
Missing SharePoint permissions
Permissions tied to source Azure AD object IDs become orphaned entries after cutover. The symptom is a user who can authenticate but cannot open a SharePoint site they previously owned. The fix is a permission remediation script run post-cutover, but the detection step must happen pre-migration. Export all site permissions before the first batch runs.
Guest access breakage
External sharing links and guest user access are not automatically preserved. Every external guest must be re-invited from the target tenant. Build this into the runbook as a named task with a business owner responsible for each site or Team.
Proactive mitigation checklist
- During discovery: audit all mailbox holds, archive sizes, shared mailboxes, and delegated permissions.
- During pre-pilot: run the cross-tenant validation script against all objects, not just the pilot set.
- During pilot: test a shared mailbox, a delegated mailbox, and a Teams channel owner — not just standard users.
- Before cutover: confirm guest access re-invite list is prepared and assigned to a business owner.
- After cutover: run a silent data loss check by comparing source and target item counts for a sample of mailboxes and OneDrive accounts.
Pro Tip: Build a silent data loss verification step into your acceptance criteria. Compare source and target item counts for a 10% sample of mailboxes and OneDrive accounts within 48 hours of each wave. A discrepancy of more than 2% warrants investigation before the next batch starts.
Key takeaways
A successful Microsoft 365 tenant migration requires correct identity mapping via CTIM, workload sequencing that starts with Exchange, and a tested rollback plan before any production batch runs.
| Point | Details |
|---|---|
| Start with identity mapping | CTIM attributes (ExchangeGUID, ArchiveGUID) must be verified before any migration batch runs. |
| Sequence Exchange first | Migrate mailboxes before or alongside Teams, as Teams content depends on mailbox infrastructure. |
| Use a two-tool approach | Native Migration Orchestrator handles bulk workloads; add MigrationWiz for Teams history and SharePoint permissions. |
| Plan for guest access remediation | External sharing links and guest access are not preserved automatically and require a dedicated re-invite workflow. |
| Engage Techbug for managed support | Techbug handles discovery, runbook authoring, execution, and post-migration support for Australian organisations. |
The reality of tenant migrations in Australia
Most of the tenant migrations that come to Techbug arrive after an internal team has already hit a wall — usually at the identity mapping stage or after a pilot that surfaced Teams history loss nobody had planned for. The pattern is consistent: the technical steps are documented, but the project scope was underestimated at discovery.
What actually makes these projects land well is treating the discovery phase as the real deliverable. A thorough discovery produces a workload inventory, an identity mapping table, a list of holds and exceptions, and a realistic timeline. Everything after that is execution against a known scope. When Techbug engages on a migration, the first output is always that discovery document, because it is the thing that prevents the 11 PM phone call three weeks later.
For Australian organisations considering a managed engagement, the right time to call is before the runbook is written, not after the first batch fails.
Techbug’s managed migration service for Australian organisations
Running a Microsoft 365 tenant migration without a tested runbook and experienced hands on the tools is where projects get expensive fast. Techbug offers end-to-end managed migration support for Australian businesses: discovery workshops, identity mapping, runbook authoring, pilot execution, production cutover, and post-migration validation.
Techbug’s team has delivered migrations across M&A, consolidation, and rebrand scenarios for Australian organisations, with outcomes including full mailbox and OneDrive migrations completed within agreed maintenance windows and SharePoint permission remediation completed within 48 hours of cutover. The engagement model is flexible: Techbug can deliver the pilot only, leaving your team to execute production, or manage the full project from discovery to decommission.
If your project involves Teams history, Power Platform, or a hard M&A deadline, get Techbug involved at the scoping stage. Contact the team through Techbug’s managed IT services page to request a discovery workshop or migration estimate. For organisations also reviewing managed IT services pricing before committing, that page covers engagement models and cost structures plainly.
Authoritative sources to use during planning
These are the core references to keep open during discovery and runbook authoring:
- Plan a Microsoft 365 tenant-to-tenant migration (Microsoft Learn) — the authoritative overview of migration approaches, workload dependencies, and coexistence planning. Start here.
- Cross-tenant identity mapping (Microsoft Learn) — the definitive reference for CTIM attribute requirements. Use during prerequisites and identity mapping steps.
- Migration Orchestrator overview (Microsoft Learn) — covers what the orchestrator moves, what it does not move, and licensing requirements.
- Cross-tenant mailbox migration (Microsoft Learn) — the full Exchange MRS runbook including PowerShell examples, batch creation, and the validation script.
- Tenant-to-Tenant M365 Migration Playbook (Pro IT NW) — an independent practitioner playbook covering timeline estimation, the two-tool pattern, and domain cutover mechanics.
- Microsoft 365 tenant-to-tenant migration without data loss (Petri) — focuses on identity reconciliation, silent data loss risks, and guest access remediation. Use during identity mapping and post-migration validation planning.
- Tenant-to-tenant migrations (Power Platform) — Microsoft’s guidance for moving Power Platform environments between tenants. Consult when Power Automate or Power Apps are in scope.
Use these as working references throughout the project, not just during initial planning. The Microsoft Learn articles are updated regularly, so check the revision date before finalising your runbook.