
A cloud-first architecture using Microsoft Intune with Windows Autopatch is the recommended approach for most Australian organisations managing Windows endpoints. For mixed or on-premises workloads, Azure Update Manager and a hybrid ConfigMgr/WSUS layer fill the gaps. Here is what that looks like in practice:
- Inventory first. Run a device discovery scan before touching any policy. You cannot manage what you have not counted.
- Select a pilot group. Aim for a small representative portion of your fleet: diverse hardware, a mix of roles, and at least one business-critical user who will tell you immediately if something breaks.
- Define update rings. Pilot, validation, broad, and catch-up. Keep deferral periods short and predictable.
- Enable reporting. Intune and Autopatch dashboards give you per-device compliance status out of the box. Turn them on before you deploy anything.
The payoff: lower operational overhead, faster security coverage (hotpatch where eligible means no restart for many monthly security fixes), and audit-ready reporting that satisfies both cyber-insurance requirements and the Australian Cyber Security Centre’s Essential Eight patching controls.
Pro Tip: If your organisation is already licensed for Microsoft 365 Business Premium or any Microsoft 365 E3/E5 plan, Autopatch entitlements are likely included. Check before purchasing additional tooling.
Table of Contents
- What does Windows update management actually cover?
- Which platforms should you use for patch management?
- What types of Windows updates do you need to handle differently?
- How do you structure a rollout that actually reduces risk?
- How do you configure Intune and Autopatch to implement this?
- How do you verify deployments and produce audit evidence?
- What do you do when a patch breaks something or a critical CVE drops?
- What does Windows update management cost in Australia?
- How Techbug runs Windows patching for Australian SMBs
- Key takeaways
- The reality of patching in Australian SMB environments
- Techbug’s managed patching service for Australian businesses
- Useful sources and further reading
What does Windows update management actually cover?
Patch management for Windows is the discipline of identifying, acquiring, testing, and deploying updates to Windows operating systems to reduce security risk and maintain compliance, as NIST defines it. That definition sounds tidy. The operational reality is messier: it spans driver updates that brick laptops, feature upgrades that break line-of-business apps, definition updates that need to land within hours, and hotpatch fixes that need no restart at all.
The functional scope covers six activities:
- Reporting — producing evidence for audits, cyber-insurance, and internal SLAs.
The primary goals are risk reduction, minimal disruption to business operations, and demonstrable compliance. Success metrics worth tracking: time-to-patch for critical CVEs, percentage of compliant devices across each ring, number of failed installs per deployment cycle, and mean time to remediate a failed device.
Unpatched systems materially increase breach risk and operational downtime. For Australian organisations, that risk is compounded by the ACSC’s Essential Eight framework, which treats application patching as a baseline control. Failing to meet it affects not just security posture but also cyber-insurance eligibility and government contract requirements.
Which platforms should you use for patch management?
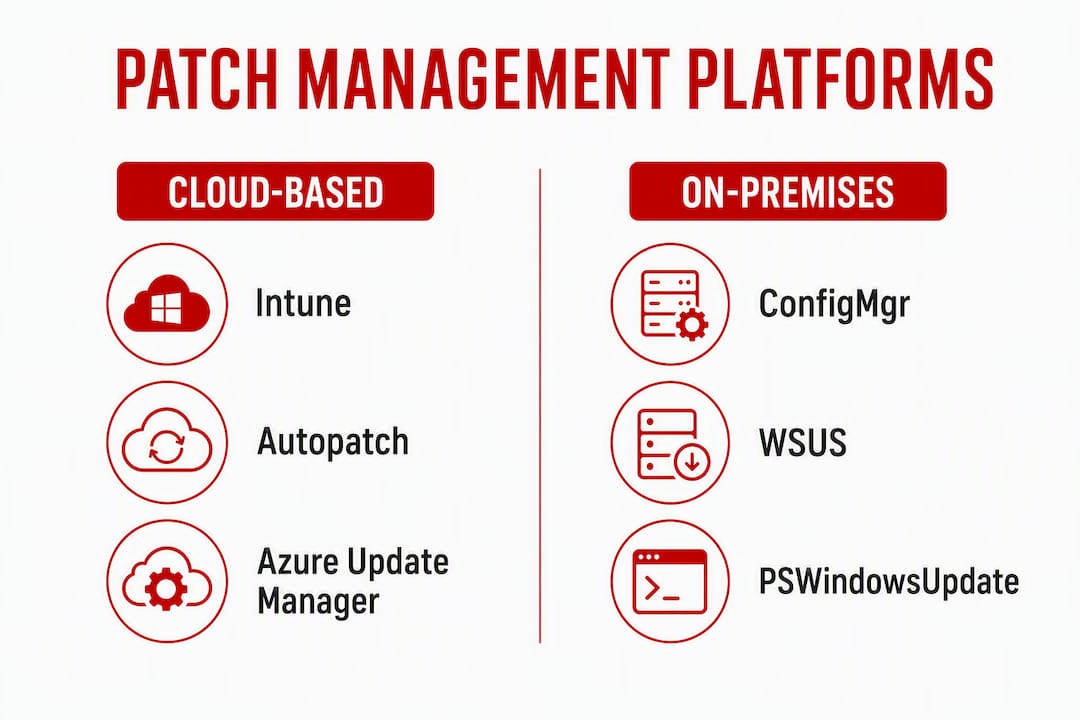
The short answer: Intune plus Autopatch for most workloads, with Azure Update Manager or ConfigMgr/WSUS for the exceptions. Here is how each platform fits.
Microsoft Intune (Windows Update for Business)
Intune coordinates policy and assignments; endpoints pull update binaries directly from Microsoft Update, not from a local server. That distinction matters for bandwidth: no on-premises distribution point, no storage overhead. Intune uses the Update Policy CSP to configure deferral periods, deadlines, active hours, and driver approval workflows. It is the default choice for cloud-joined or hybrid Azure AD-joined fleets.
Windows Autopatch
Autopatch sits on top of Intune and automates the sequencing of feature, quality, driver, and Microsoft Teams updates across phased deployment groups. It handles the ring logic for you, provides enhanced compliance reporting, and supports expedited policies for urgent CVEs. Hotpatch is enabled by default for eligible devices, meaning many monthly security updates apply without a restart. For most Australian SMBs and mid-market organisations, Autopatch removes the manual overhead of ring management.
Azure Update Manager
Azure Update Manager targets Azure-hosted VMs and multi-cloud or Arc-connected servers. If your organisation runs workloads in Azure or across AWS/GCP alongside Windows Server, this is the right tool for server-side patching. It does not replace Intune for endpoint management but complements it for infrastructure.
Microsoft Endpoint Configuration Manager (ConfigMgr / SCCM)
ConfigMgr remains relevant for organisations with isolated networks, regulatory constraints that prohibit cloud connectivity, or large software distribution requirements beyond patching. It integrates with WSUS for update approval and distribution, and it supports complex deployment rules that cloud-only tools cannot match. The trade-off is infrastructure overhead: SQL Server, distribution points, and a dedicated team to maintain them.
WSUS (Windows Server Update Services)
WSUS is the on-premises approval and caching layer that ConfigMgr typically sits in front of. On its own, WSUS is adequate for small, isolated environments but lacks modern compliance reporting and requires manual ring management via Group Policy. Cloud-native designs replace WSUS for most workloads, reducing local bandwidth and storage requirements significantly.
Supplementary tools
is a PowerShell module useful for scripted scans, targeted installs on special-case endpoints, and emergency intervention on devices that have fallen out of policy. Third-party patch managers (for non-Microsoft applications) fill the gap Intune and Autopatch leave for software like Adobe Acrobat, Chrome, or Java.
| Platform | Best for | Deployment model | Automation level | Reporting / compliance | Operational overhead | Licensing shape |
|---|---|---|---|---|---|---|
| Intune + WUfB | Cloud-joined SMB to enterprise | Cloud-native | Policy-driven, manual ring config | Good: per-device status, compliance reports | Low | Included in M365 Business Premium, E3/E5 |
| Windows Autopatch | Organisations wanting automated ring management | Cloud-native | High: automated sequencing, hotpatch | Enhanced: expedite, hotpatch, rollout reports | Very low | Requires Intune + Windows 10/11 Pro or Enterprise |
| Azure Update Manager | Azure VMs, Arc-connected servers | Cloud / multi-cloud | Moderate: scheduled maintenance windows | Good: per-resource compliance | Low to moderate | Pay-per-use or included in Defender for Servers |
| ConfigMgr / SCCM | Complex on-prem, isolated networks | On-prem / hybrid | Moderate: rule-based deployment | Strong: custom reports, SCCM dashboards | High | System Center licence + CALs |
| WSUS standalone | Small isolated networks, air-gapped | On-prem | Low: manual approval | Basic: built-in reports only | Moderate | Free (Windows Server role) |
What types of Windows updates do you need to handle differently?
Not all updates carry the same risk or urgency. Treating them the same way is one of the fastest routes to either a security gap or a broken production environment.
- Feature updates (major OS versions, e.g. Windows 11 24H2) are planned OS rollouts. Treat them like a project: pilot ring first, application compatibility scan before deployment, phased scheduling across rings over weeks, not days. Autopatch supports phased feature update rollouts and can hold devices to a minimum version while you validate.
- Quality and security updates (monthly cumulative, “B-release” Patch Tuesday) are the core of your patching cadence. Aim for rapid testing and deployment. For critical CVEs, use expedited policies to bypass normal deferral windows.
- Driver and firmware updates carry hardware regression risk. Control these via approval workflows rather than automatic deployment. Test on representative hardware before broad rollout, and keep a rollback path ready.
- Definition updates (Windows Defender antivirus signatures) and Microsoft Store app updates are typically automatic. Monitor for exceptions but do not gate them behind manual approval — they need to land quickly.
- Hotpatch updates apply many monthly security fixes without requiring a restart, when devices meet eligibility conditions. Hotpatching can significantly speed compliance for monthly security updates on eligible devices. Know your eligibility (Windows 11 Enterprise 24H2 and later, Intune-managed) and opt in deliberately.
How do you structure a rollout that actually reduces risk?
The ring model is the standard approach, and it works precisely because it limits blast radius. A bad update that breaks 3% of your pilot fleet is a recoverable incident. The same update hitting your entire organisation on a Monday morning is not.
The four-ring model
- Pilot ring (5–10% of devices): small, diverse, includes at least one device from each hardware family and business unit. Industry best practice emphasises a small, diverse pilot group as the single most effective way to catch compatibility issues before broad deployment.
- Validation ring (15–20%): broader coverage, more business-critical roles, longer soak time.
- Broad ring (remaining managed devices): deploys after validation passes without incident.
- Catch-up ring: targets devices that missed the main deployment window due to being offline or in maintenance mode.
Pilot selection criteria
Pick devices that represent your real environment: different hardware vendors, a mix of Windows 10 and Windows 11 if both are in use, users who run your most critical line-of-business applications, and at least one remote worker on a variable connection. Avoid selecting only IT staff — they are not representative of how the rest of the business uses the machines.
Typical timelines
For quality/security updates: 3–5 business days in pilot, 5–7 days in validation, then broad. For feature updates: 2–4 weeks in pilot, 2–4 weeks in validation. Schedule maintenance windows outside core Australian business hours (6:00 AM–8:00 AM AEST works well for most organisations; avoid Monday mornings).
Keeping policy simple
Over-configuration is a real problem. Policies with long, varying deferral periods and complex deadline logic create gaps and user friction. Prefer short, predictable deferrals (7 days for quality updates in pilot, 14 days for broad) and consistent deadlines. The Windows 10 update policy pitfalls that cause the most disruption almost always trace back to over-engineered ring configurations, not under-engineered ones.
Pro Tip: Document your ring membership in a spreadsheet or Entra group description. When a device falls into the wrong ring, you will know immediately rather than discovering it three months later during an audit.
Phased release checklist
- Confirm prerequisites (Entra join state, telemetry level, Intune enrolment).
- Define rollback path before deployment starts.
- Brief business owners on maintenance windows.
- Prepare monitoring runbook: what to check, who to call, when to pause.
- Deploy to pilot. Wait. Check reports. Only then proceed.
How do you configure Intune and Autopatch to implement this?
Translating ring strategy into Intune policy is straightforward once you know which policy type does what.
Policy types in Intune
- Update rings policy (Update Policy CSP): controls deferral periods, deadlines, active hours, and restart behaviour for quality and feature updates. This is your primary lever for ring management in Intune.
- Feature update policy: pins devices to a specific Windows version or controls the timing of major OS upgrades independently of quality updates.
- Quality update policy: manages monthly cumulative updates, including expedited deployment for urgent CVEs.
- Driver update policy: controls driver and firmware approvals, with options for automatic or manual approval per driver class.
Autopatch groups vs. Intune update rings
Autopatch groups are the Autopatch-native equivalent of Intune update rings. If you enable Autopatch, it creates and manages its own deployment groups (Test, Ring 1, Ring 2, Ring 3, Last). You can customise membership and add custom groups. Use dynamic Entra groups to automate membership based on device attributes (department, location, hardware model) rather than maintaining static lists.
Configuration sequence
- Inventory and prerequisites: confirm all devices are Entra-joined (or hybrid-joined), enrolled in Intune, and reporting the required telemetry level (at minimum, “Required” diagnostic data for Autopatch).
- Create pilot group: build an Entra dynamic group scoped to your pilot devices.
- Configure update ring: set deferral periods (7 days for pilot quality updates), deadlines (3 days after deferral expires), and active hours matching your business schedule.
- Enable hotpatch: for eligible Windows 11 Enterprise 24H2+ devices, enable the hotpatch policy in Intune. Verify eligibility in the Autopatch hotpatch report.
- Enable expedite policy: configure a quality update expedite policy for critical CVEs. This bypasses normal deferral windows and targets devices immediately.
- Monitor: check the Intune update compliance report and Autopatch deployment report after each Patch Tuesday cycle.
Common misconfigurations to check
- Telemetry set below “Required” breaks Autopatch reporting.
- Devices not Entra-joined (still domain-only) cannot use Autopatch.
- Conflicting Group Policy Objects overriding Intune CSP settings — check for legacy GPOs that set Windows Update server URLs to a WSUS address.
- Windows Update client policies applied via both GPO and MDM simultaneously cause unpredictable behaviour; pick one delivery method and stick to it.
How do you verify deployments and produce audit evidence?
Effective patch management requires continuous operations, not a one-time project; compliance reporting is the mechanism that proves it. For Australian organisations subject to the Essential Eight or cyber-insurance requirements, retained evidence of deployments and approvals is not optional.
Key reports to collect
| Report | Source | What it shows |
|---|---|---|
| Per-policy compliance | Intune / Autopatch dashboard | % devices compliant per update ring |
| Device update status | Intune device reports | Per-device install state, last check-in |
| Failed installs | Intune / ConfigMgr reports | Devices with persistent update failures |
| Rollout progress | Autopatch deployment report | Ring-by-ring deployment progress |
| Hotpatch report | Autopatch hotpatch dashboard | Eligibility and hotpatch adoption rate |
| Windows event logs | Endpoint (Event Viewer / WMI) | Local install history, error codes |
Audit evidence to retain
- Per-device update history (exported from Intune or ConfigMgr on a regular schedule).
- Deployment approval records (who approved, when, for which update).
- Pilot test results and sign-off documentation.
- Remediation tickets for failed devices.
Keep this evidence for at least 12 months. Cyber-insurance assessors and ACSC Essential Eight auditors will ask for it. Linking your IT compliance practices to your patching evidence trail is the difference between passing an audit quickly and scrambling for records.
SIEM and ITSM integration
Feed update telemetry and compliance alerts into your SIEM (Microsoft Sentinel, Splunk, or similar) and ITSM (ServiceNow, Jira Service Management) for automated remediation workflows and continuous audit trails. A device that has not checked in for 14 days should trigger an alert, not a manual weekly report review.
What do you do when a patch breaks something or a critical CVE drops?
Both scenarios require a pre-built runbook, not improvisation under pressure.
Emergency patch deployment
- Identify the CVE severity and affected device scope using Intune vulnerability reports or Microsoft Security Update Guide.
- Escalate approval through your change management process — for critical CVEs, this should be a fast-track path, not the standard 5-day window.
- Use the Autopatch expedite policy or a targeted Intune quality update policy scoped to affected devices. This bypasses normal deferral periods.
- Communicate to stakeholders: what is being patched, when maintenance windows will occur, and what the expected impact is.
- Confirm compliance via the Intune expedite report within 24–48 hours of deployment.
Rollback options
- Uninstall a quality update: available via Intune’s “Uninstall update” action for a limited window after deployment (typically 30 days for quality updates, 60 days for feature updates).
- Feature update rollback: Windows 11 supports a 10-day rollback window post-upgrade via Settings. For managed devices, trigger this via Intune or a PowerShell script.
- System restore / OS rollback: use for severe regressions where the uninstall path is unavailable. Requires restore points to be enabled — verify this in your baseline policy.
- Restore from backup: the last resort for catastrophic failures. This is why cloud backup is part of any serious patching programme, not an afterthought.
Pro Tip: The Windows 10 1809 release is a well-documented example of a feature update that deleted user files on some configurations. A pilot-first approach would have caught this before broad deployment. Never skip the pilot ring for feature updates, regardless of time pressure.
Troubleshooting stuck updates
When a device fails to update repeatedly, the most common culprits are a corrupted Windows Update component store (SoftwareDistribution folder or catroot2) or a broken Windows Update service. Use supported repair tools (DISM, SFC, the Windows Update Troubleshooter) to reset these components. Ad-hoc registry edits are tempting but create inconsistent states that are harder to diagnose later. For persistent failures, isolate the device, repair the component store, re-enrol in Intune if necessary, and document the remediation.
For critical servers or network appliances, consider patching offline in a maintenance window with the device isolated from production traffic. This is especially relevant for domain controllers and network infrastructure where a failed update could cascade.
What does Windows update management cost in Australia?
Licensing and infrastructure costs vary significantly depending on your chosen architecture.
Cloud-native (Intune + Autopatch)
- Intune is included in Microsoft 365 Business Premium, Microsoft 365 E3, E5, and EMS E3/E5. If you are already paying for one of these SKUs, Autopatch entitlements come with it.
- Autopatch requires Windows 10/11 Pro or Enterprise, Intune enrolment, and the required diagnostic telemetry. No additional licence fee beyond the Intune entitlement.
- Bandwidth savings: because endpoints pull directly from Microsoft Update rather than a local WSUS server, you eliminate the storage and bandwidth overhead of caching update binaries on-premises.
On-premises (ConfigMgr / WSUS)
- WSUS is a free Windows Server role, but it requires a Windows Server licence, storage for cached updates, and ongoing maintenance effort.
- ConfigMgr requires System Center licences and Client Access Licences (CALs), plus SQL Server infrastructure. For organisations already running ConfigMgr for software deployment, the marginal cost of using it for patching is low. For organisations starting fresh, the infrastructure investment is substantial.
Hidden operational costs
- Pilot and testing labour: even with Autopatch, someone needs to review reports and sign off on ring progression.
- Rollback and remediation effort: budget for 2–5% of devices requiring manual intervention per deployment cycle in a mixed estate.
- Third-party patching: Intune and Autopatch cover Microsoft products. Non-Microsoft applications (Adobe, Chrome, Java, line-of-business software) require a separate patching tool or process.
Procurement brief essentials for Australian IT teams: Before engaging a vendor or managed provider, document your expected device count, required support SLAs (particularly for after-hours emergency response), reporting requirements for cyber-insurance or Essential Eight compliance, and any regulatory constraints (e.g. data sovereignty requirements that affect cloud connectivity). Australian organisations in regulated sectors (finance, health, government) may face additional constraints on telemetry data leaving Australian borders — confirm this with your legal or compliance team before committing to a cloud-native architecture.
How Techbug runs Windows patching for Australian SMBs
The following checklist reflects the operational approach Techbug uses when managing patch deployment for clients across Australia. It is designed to be handed to an in-house IT team or used as a briefing document for a managed provider.
Operational checklist
- Device discovery and inventory: run a full discovery scan using Intune device reports or a network scanner. Document OS versions, hardware models, and current patch states.
- Application compatibility scan: identify applications known to have issues with the target update (check vendor release notes and Microsoft’s compatibility database).
- Pilot group selection: select 5–10% of devices covering diverse hardware, roles, and locations. Include at least one business-critical user.
- Test and validation criteria: define pass/fail criteria before deployment starts. Typical criteria: no application crashes, no login failures, update installs within the expected window, device checks in to Intune within 24 hours post-install.
- Policy creation: configure update rings in Intune with appropriate deferral periods and deadlines. Document the policy settings and approval chain.
- Staged deployment: deploy to pilot, wait for soak period, review reports, proceed to validation, then broad.
- Monitoring and remediation: check compliance reports daily during active deployment. Remediate failed devices within the SLA window (typically 48–72 hours for quality updates, 5 business days for feature updates).
Roles and responsibilities
Assign clear ownership before deployment starts. Typically: an IT administrator owns policy creation and monitoring; a change manager or business owner approves ring progression; a helpdesk team handles end-user remediation. In a managed service model, Techbug holds the policy and monitoring role, with client sign-off on ring progression and major feature updates.
What Techbug retains for client audits
Per-device update history, deployment approval records, pilot test results, and remediation tickets. These are retained and available for client review at any time, satisfying both cyber-insurance assessors and Essential Eight audit requirements.
Managed service vs. in-house
For organisations with fewer than 50 devices or without a dedicated IT administrator, managed patching is almost always more cost-effective than in-house operations. The break-even point shifts as device count grows and internal IT capacity increases. Techbug’s managed IT services include patch management as a core component, with clear handover documentation if a client later builds internal capability.
Pro Tip: When briefing a managed provider, ask specifically what they retain as audit evidence and how quickly they can produce it. “We manage your patches” is not the same as “we can show an auditor every approval and deployment record for the past 12 months.”
Key takeaways
A cloud-first Intune and Autopatch architecture is the most practical and cost-effective approach to Windows update management for most Australian organisations, with ConfigMgr or WSUS retained only for isolated or regulated workloads.
| Point | Details |
|---|---|
| Cloud-first is the default | Intune plus Autopatch covers most Australian workloads with lower overhead than on-prem WSUS or ConfigMgr. |
| Pilot testing prevents most failures | A small, diverse pilot group catches compatibility issues before they reach the broad fleet. |
| Hotpatch reduces downtime | Eligible Windows 11 Enterprise devices can receive many monthly security fixes without a restart. |
| Audit evidence must be continuous | Retain per-device update history, approval records, and remediation tickets for at least 12 months. |
| Techbug manages this end-to-end | Techbug’s managed IT services include policy design, staged rollout, compliance reporting, and emergency response for Australian SMBs. |
The reality of patching in Australian SMB environments
The gap between how patch management is described in vendor documentation and how it actually runs in a 30-seat Australian business is significant. Most SMBs do not have a dedicated test environment. Their device estate is a mix of hardware generations, some machines are only online intermittently, and the person responsible for patching is also handling helpdesk tickets, firewall rules, and the CEO’s printer.
That context shapes every policy decision. Short deferrals beat long ones because they are easier to explain and easier to enforce. Conservative feature update schedules are not laziness; they are a rational response to limited rollback capacity. Hotpatch is genuinely valuable in this environment precisely because it removes the restart negotiation with business owners who refuse to reboot during business hours.
The other thing vendor documentation underplays: the importance of negotiating maintenance windows with the business, not just setting them technically. A maintenance window that fires at 2:00 AM on a machine that is always switched off at 5:00 PM achieves nothing. The best patch policy is one the business will actually tolerate, documented in writing, and reviewed every six months.
Centralised reporting matters more than most SMBs realise until they face an insurance claim or an audit. The question is never “are you patching?” It is always “can you prove it?” Build the evidence trail from day one, not after the first incident.
Techbug’s managed patching service for Australian businesses
Running a structured patch programme in-house takes time most Australian SMBs do not have. Techbug’s managed IT security services cover the full patching cycle: device inventory, policy design, pilot testing, staged rollout, compliance reporting, and emergency response for urgent CVEs. The approach is vendor-agnostic, which means the recommendation is always the right tool for your environment, not the one that generates the most licence revenue.
For organisations that need to demonstrate Essential Eight compliance or satisfy cyber-insurance patching requirements, Techbug retains audit-ready evidence for every deployment. No scrambling for records when an assessor asks.
If you are unsure whether your current patch programme would pass an audit, or you want to move from ad-hoc updates to a structured, reportable process, get in touch with Techbug to discuss a managed patching assessment or ongoing managed IT engagement.
Useful sources and further reading
- Windows update and patching — Australian Signals Directorate Blueprint
- ACSC Essential Eight — Australian Cyber Security Centre
- Hardening Microsoft Windows workstations — cyber.gov.au
- Windows update management overview — Microsoft Intune
- Windows Autopatch overview — Microsoft Learn
- Windows Update client policies — Microsoft Learn
- Manage Windows quality updates — Microsoft Intune
- Update Policy CSP — Microsoft Learn
- WSUS deployment guide — Microsoft Learn
- NIST — patch management guidance
- Techbug managed IT services — Brisbane
- Techbug IT security services